Repository navigation
ci: add an optional npm dependency report - #253
PresentJay wants to merge 1 commit into
Conversation


|
I contribute to zero-shelter. For shx, I am proposing an optional HTML view of npm advisories alongside the existing Node and operating-system compatibility checks. Would you use a report like this when reviewing the dependency tree? I can withdraw it if the separate manual workflow would mostly duplicate your current process. |

|
Could you help me understand what the npm dependency report would look like? Perhaps you could run this locally for shx, take a screenshot, and attach the image here so I can get a sense for what this is. I'm not sure this would be useful for me since I already run |
|
Thanks for the suggestion. Here is a local shx report from 2026-11-16 UTC, using this PR’s tree (
It uses npm audit alone: 30 raw advisory records become 20 displayed findings, with none accepted into a baseline. This adds no scanner coverage over your existing npm audit; the value to judge is the presentation. The “none published” labels are not a verified claim that no upstream fix exists. That wording is a limitation of this preview. |
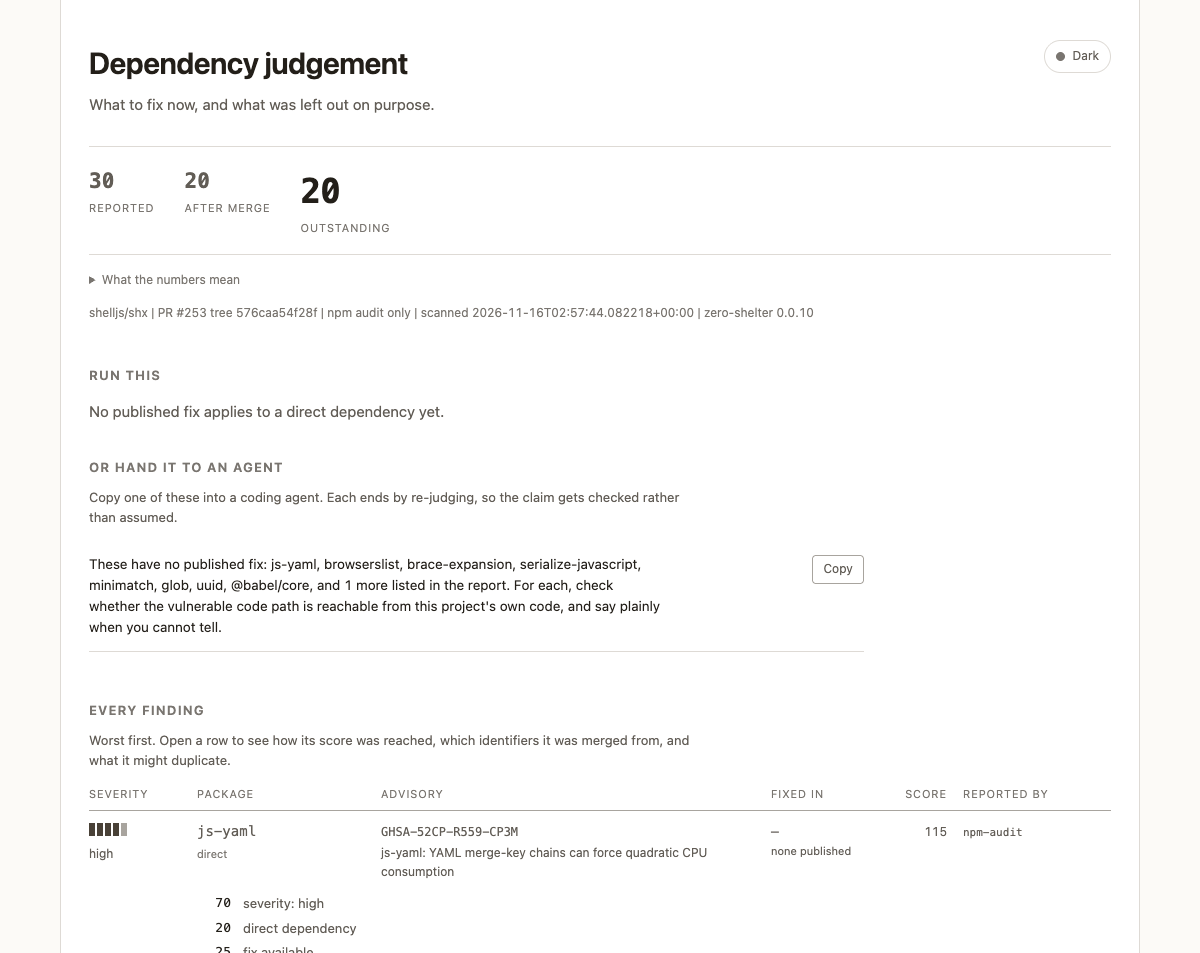


shx already has a Node and operating-system compatibility matrix. I tried its committed npm tree separately to see whether a downloadable advisory report would be useful alongside those behavior checks. I contribute to zero-shelter, the tool proposed here, and used AI assistance for this change and validation.
The PR adds only
.github/workflows/dependency-report.yml. Maintainers choose when to run Dependency triage report usingworkflow_dispatch; it requestscontents: read.npm audit --package-lock-only --ignore-scriptssupplies one npm report to pinnedzero-shelter@0.0.10, which produces HTML retained for 7 days. No project dependencies are installed, no project lifecycle scripts or shx commands are run, and no baseline is accepted. Finding exit1and judgement-error exit2fail this manual job. Node 24 is used only for this report job.The stored capture at
3829f83e1498contained 30 raw records, 20 merged findings and 20 outstanding findings. Audit, JSON and HTML commands exited1. YAML, shell syntax and diff checks passed, with manifest and lockfile unchanged. This rewrite includes no fresh scan. Application tests, the compatibility matrix and a hosted manual run were not verified in that validation.The report uses npm advisories only and makes no runtime reachability claim. Audit sends package/version metadata to the configured registry.
npxdownloads and executes third-party CLI code in CI; read-only repository permissions do not remove that execution risk.Does a separate manual advisory report fit how you maintain shx? I can withdraw it if the extra workflow would be redundant.