
Chock policies as Codex plugins — a real PreToolUse deny hook for guards, a Stop gate for writes, both held untrusted until you approve them.


An agent you're running can already touch your shell, your git history, and your CI config.
You want it to move fast without being the reason a stray helm uninstall actually happens.
Telling it to be careful in a prompt is not a guarantee; a plugin that can refuse the command
is closer to one — a matched destructive command is denied before it runs, witnessed on a
real Codex Desktop install (Windows, 2026-08-24). Gate policies work differently here: Codex
records no file-writing tool vocabulary, so they cannot judge the write itself and are wired at
Stop instead, re-reading what the turn left on disk.
Codex makes you approve this first. Codex installs every hook UNTRUSTED. Until you open a
plugin's page and approve its hook ("needs review before it can run" → Trust), the plugin is
advisory text only — the trust is bound to a hash of the hook command, so an update silently
voids it. A hook that cannot run at all (missing python3, timeout) fails open: Codex allows it. A
guard that runs and crashes is a deny here, because Codex rejects the confirmation prompt
other clients show, and a gate that cannot reach a decision refuses rather than allowing
something it never judged.
Codex reads this repository as a git marketplace, the same mechanism as its Plugins UI:
# ~/.codex/config.toml
[marketplaces.chock-codex]
source_type = "git"
source = "https://github.com/open-coder-ai/chock-codex-plugins.git"
Then install plugins from the chock-codex marketplace in the Plugins UI, and approve each
guard's hook trust review.
See PLUGINS.md for the full list: each policy, its version, and whether it
enforces or advises in this client. A plugin governs one session; it doesn't run in CI or
travel with a clone. For enforcement that follows the repository, with no trust toggle to
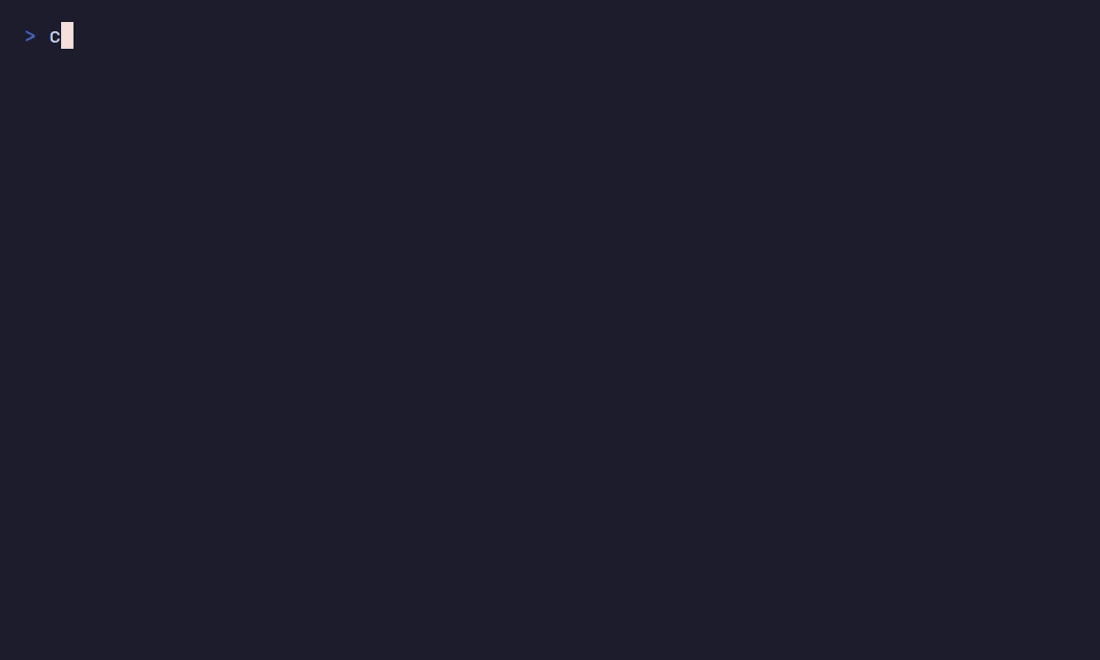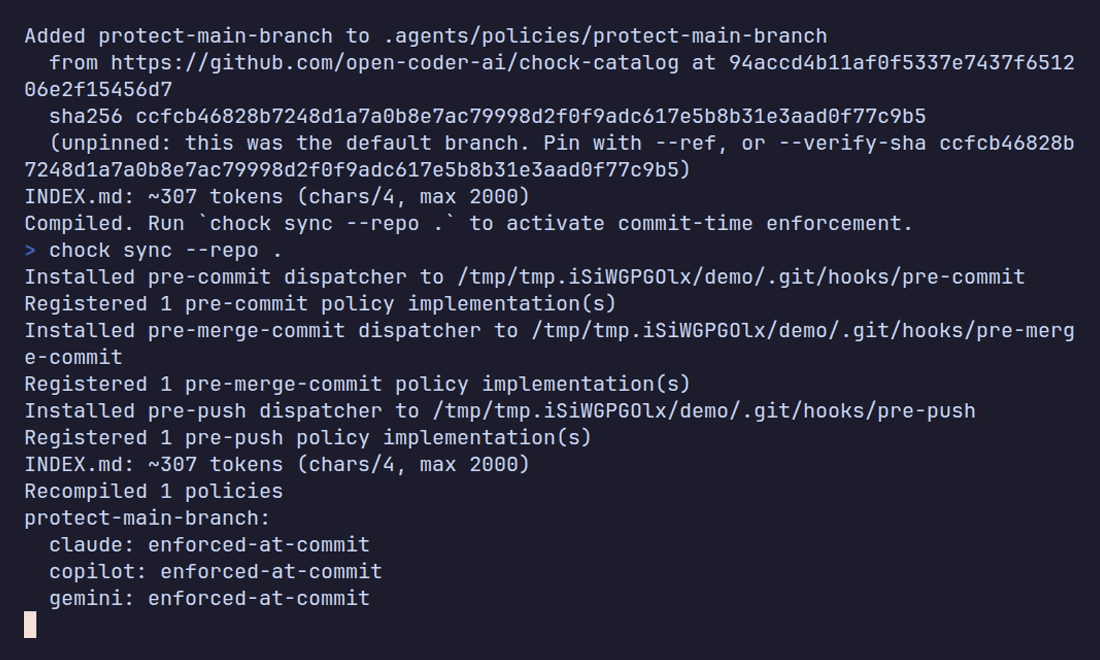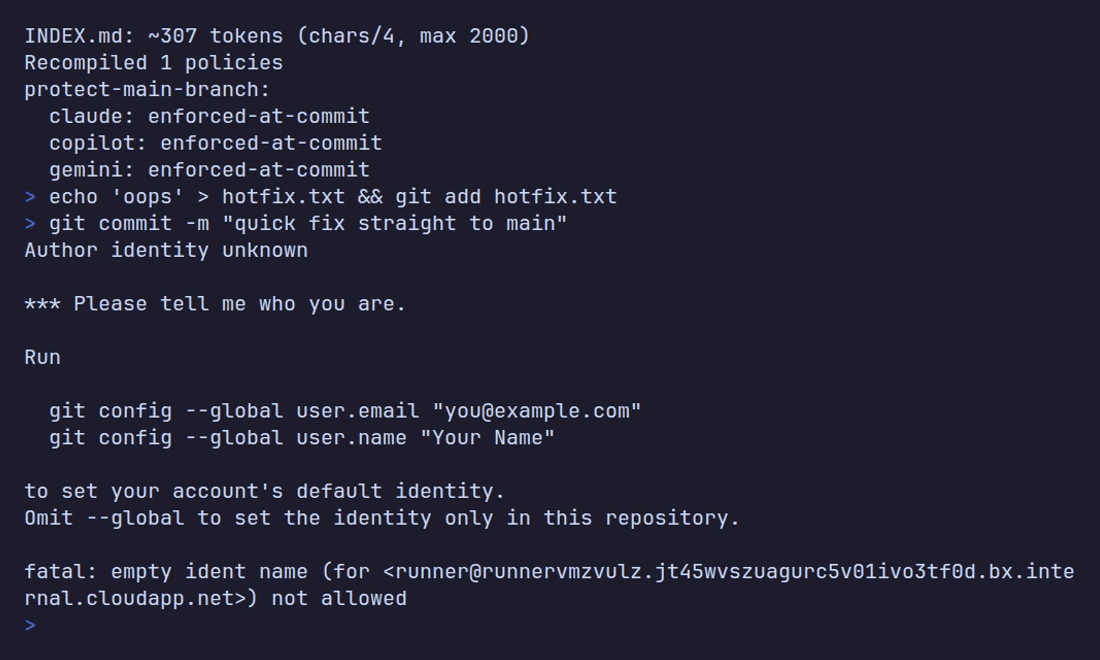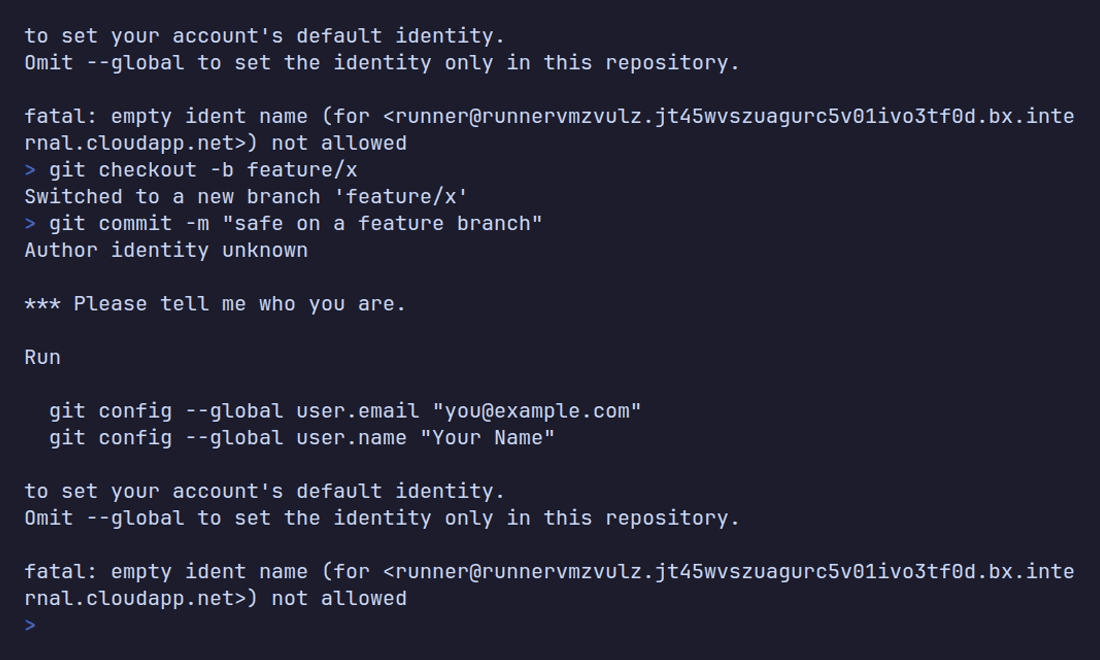
forget, install Chock directly: pip install chock && chock init && chock sync --ci.
Every file here is compiled from policy sources in chock-catalog by chock. Pull requests against this repository are closed automatically — open them against the catalog instead.
- Generated only: CI regenerates from the pinned catalog and fails on any difference.
- Byte-identical guards: each guard script is a verbatim copy of its policy's source in the catalog, and the hook adapter a verbatim copy of its framework source.
- Best-effort, not a boundary: guards are pattern-based filters; see SECURITY.md.
- Tested upstream, and gated: every policy ships an eval suite
(
base/<policy>/evals/suite.yaml) in the catalog, and the publish workflow runschock checkandchock check --only evalsbefore packaging anything — a policy whose evals fail cannot reach this repository. The tests live in the catalog because the policy source does; this repository is compiled output. - This README is hand-written, as are
SECURITY.mdand the workflows under.github/, so they sit outside the generated-only guarantee.
Nothing above asks for trust that cannot be checked. This rebuilds the published tree from source and compares it with what is committed here:
git clone https://github.com/open-coder-ai/chock-codex-plugins dist
git clone https://github.com/open-coder-ai/chock-catalog catalog
git clone --branch "$(tr -d '[:space:]' < catalog/.framework-ref)" \
  https://github.com/open-coder-ai/chock framework
pip install ./framework
chock plugin build --repo catalog --policies-dir base --format codex --out-dir dist
chock marketplace build --dist dist --tree codex
git -C dist diff --exit-code && git -C dist status --porcelain
Silence from both git commands means this repository is byte-identical to a fresh build
from the catalog. The framework ref comes from the catalog's own .framework-ref, which is
what the publish and Generated-only workflows read, so this recipe cannot drift from the
release a tree was actually built with.
chock-market.lock records a sha256 per published plugin directory, so one package can be
checked without rebuilding the rest.
If you are listing these plugins in a marketplace, pin both a tag and the full commit SHA. The tag names the release; the SHA is what holds the reviewed bytes still.
| You want to | Go to |
|---|---|
| Fix or add a policy | chock-catalog — it reaches every client from there, including this one |
| Report that a guard did or did not block on your Codex version | an issue on chock, which records the witnessed-blocking claims these packages carry; "it fails open where you say it fails closed" is the most useful result you can send |
| Report a bug in how packages are generated | chock, where the emitter lives |
| Fix this README | here — it is hand-written, not generated |
| agentseam | the primitives — one handler API and a verified capability matrix across 16 agents |
| chock | the compiler — one policy into git hooks, CI gates and native pre-tool hooks |
| chock-catalog | the policies — 42, each labelled enforced or advisory, with replayed evals |
| context-report | the evidence — a signed report of whether an agent artifact actually works |
| chock-threat-intel | the threat ledger the catalog's policies answer to |
| chock-{claude,cursor,copilot,codex}-plugins | the catalog, packaged for each agent's plugin format (generated) |
| chock-quickstart · chock-example | template repos: what chock init leaves behind, and a full adoption |
Apache-2.0, same as the framework and the catalog.