
All glory and honor to God יהוה in the name of Yeshua the Messiah (Jesus Christ).
Intelligent, Security-Conscious, and Designed for Effortless Productivity — Because With Rullst, We Rule!


Quickstart · Start building · Rullst Academy · Live examples · Documentation · Discord
cargo install cargo-rullst --version '^12' --locked
cargo rullst new my_app    # choose Blank/API, Blog, SaaS, LMS, Portfolio or ERP
cd my_app
cargo rullst dev           # rebuilds and restarts every time you save
That's it: a running application, generated as readable Rust you can change —
no hidden runtime magic. The selector installs the latest stable v12 CLI; use a
full version such as --version 12.1.2 to reproduce a specific release.
Installation and prerequisites · Zero-to-Hero tutorial · Build a JSON REST API · CLI reference
Stuck? cargo rullst doctor checks the Rust toolchain and the optional tools
Rullst uses, cargo rullst --help lists every command, and cargo rullst alone
opens an interactive menu.
Prefer an interactive dashboard? Run cargo rullst dash
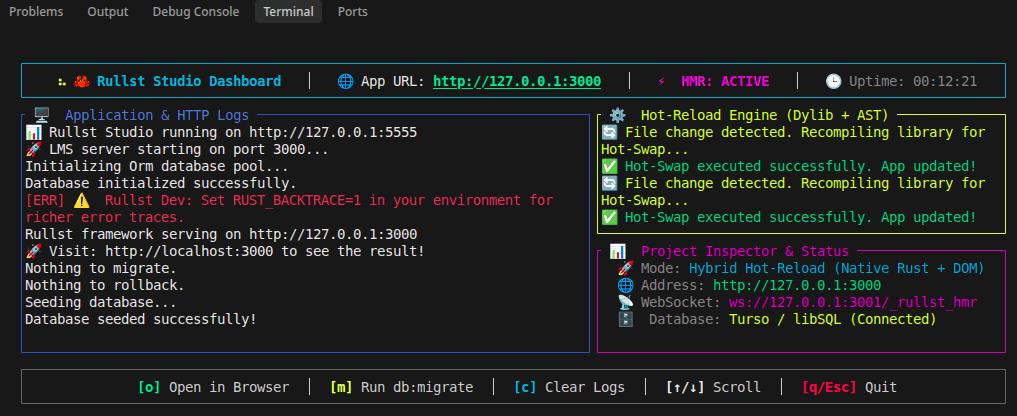
Recorded screenshot; layout and controls can differ by version. Development workflow.
use rullst::{html, response::Html, routes, Server};

async fn home() -> Html<String> {
    Html(html! {
        <div class="min-h-screen bg-slate-900 text-emerald-400 flex flex-col items-center justify-center font-sans">
            <h1 class="text-5xl font-extrabold mb-4">"Hello, Rullst! 📜🦀"</h1>
            <p class="text-slate-400 text-lg">"Your first typed route is running."</p>
        </div>
    })
}

#[tokio::main]
async fn main() -> Result<(), Box<dyn std::error::Error>> {
    let app = routes![
        get("/" => home)
    ];

    Server::new(app).run(3000).await?;
    Ok(())
}
HTML lives in a compile-time html! macro, routes are typed and pages are
server-rendered — HTMX-ready, with no JavaScript bundle to build. This snippet
comes from the Zero-to-Hero tutorial,
and every tutorial's Rust code is compiled in CI.
Prefer a JSON API?
use rullst::{Server, ServerError, routes, server::Json};
use serde::Serialize;

#[derive(Serialize)]
struct HealthResponse {
    status: &'static str,
    framework: &'static str,
}

async fn health() -> Json<HealthResponse> {
    Json(HealthResponse {
        status: "ok",
        framework: "Rullst",
    })
}

#[tokio::main]
async fn main() -> Result<(), ServerError> {
    let app = routes![
        get("/api/health" => health),
    ]
    .layer(rullst::server::from_fn(
        rullst::security::headers_middleware,
    ));

    Server::new(app).run(3000).await
}
curl http://127.0.0.1:3000/api/health
# {"status":"ok","framework":"Rullst"}
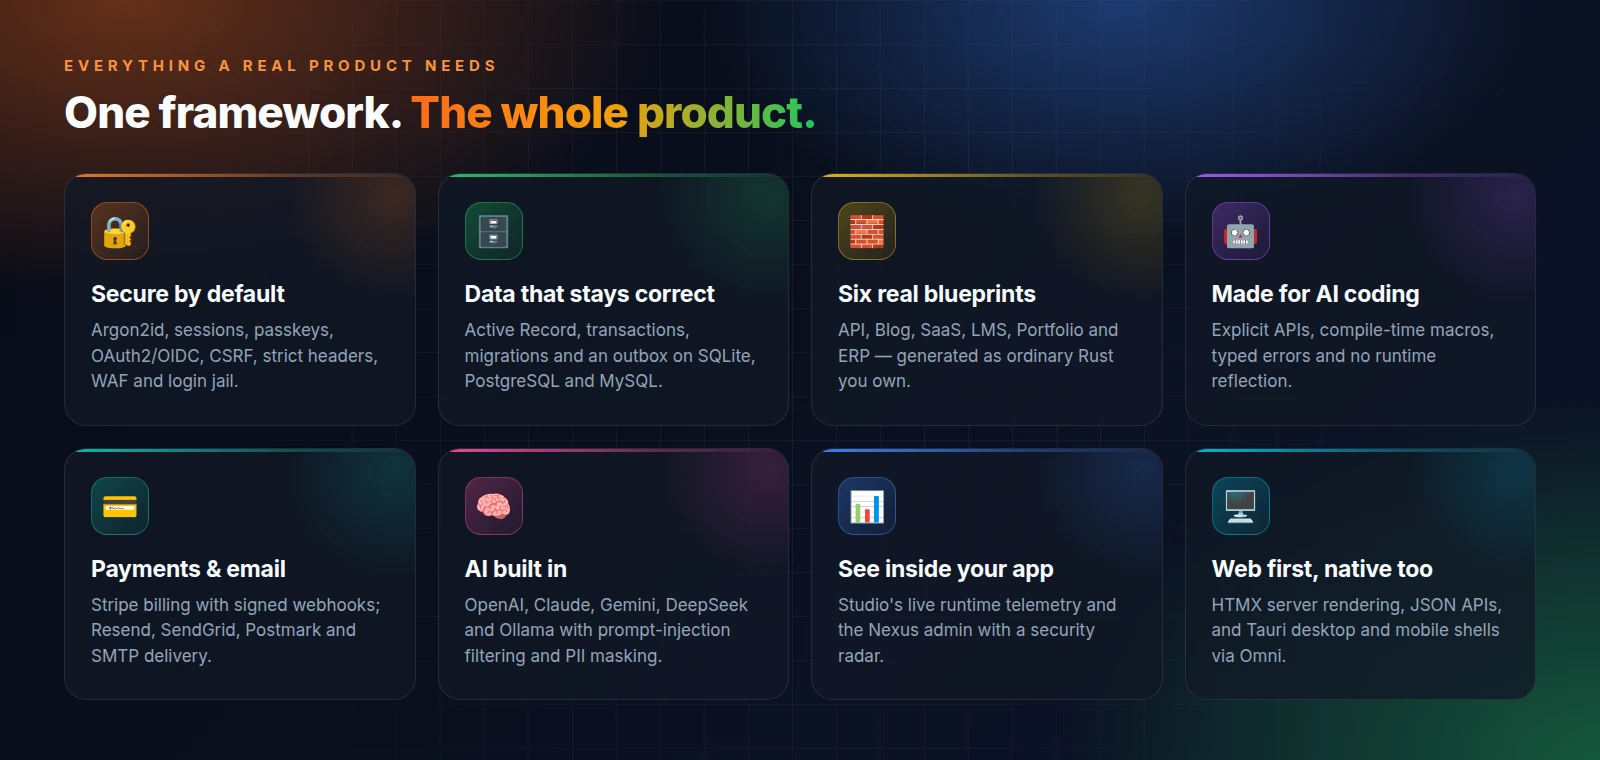
Every capability has a documented boundary — security middleware does not replace your authorization rules, and databases are not interchangeable. See the capability ledger · Why Rullst? · Axum & SQLx escape hatches
Real applications running today, every one of them built with Rullst. Click to explore — their code and deployment recipes live in Rullst/examples.
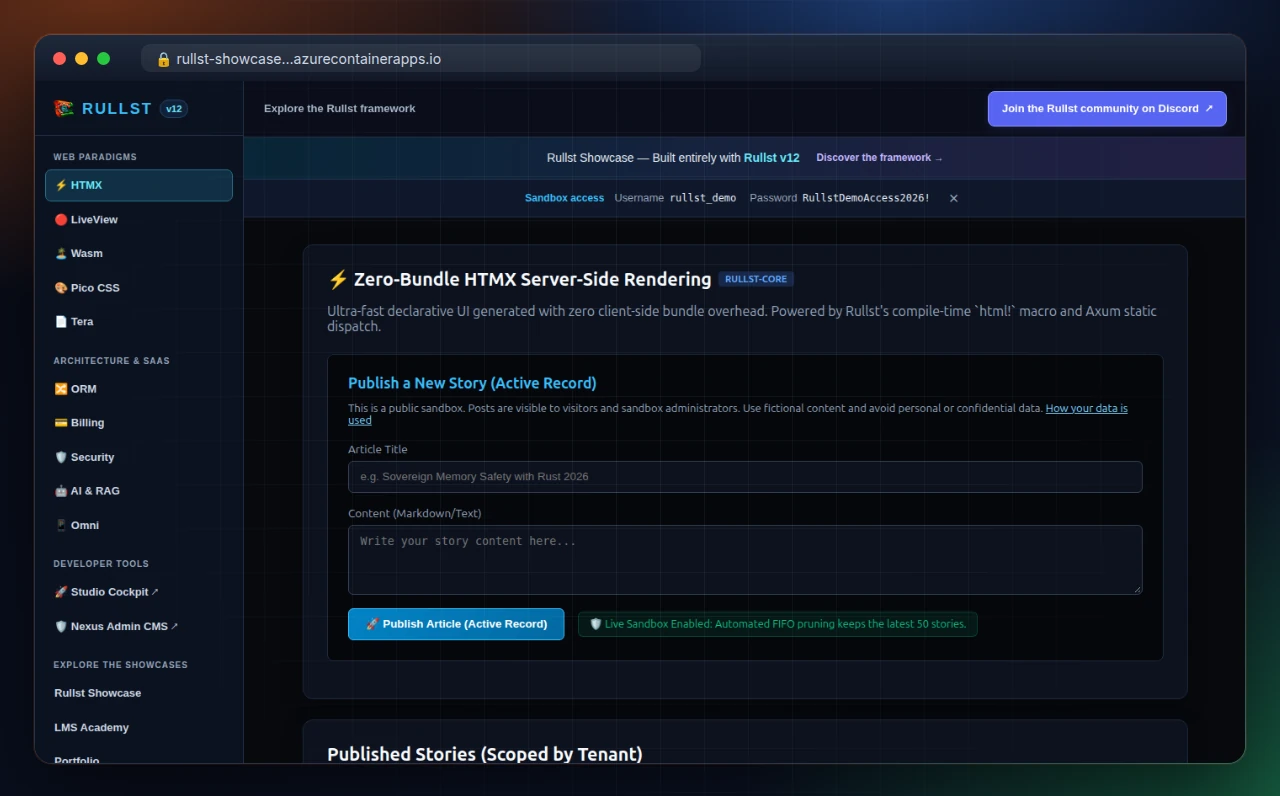
🌐 Showcase — SSR, LiveView, Wasm, ORM, billing, security and AI demos · Open ↗ |
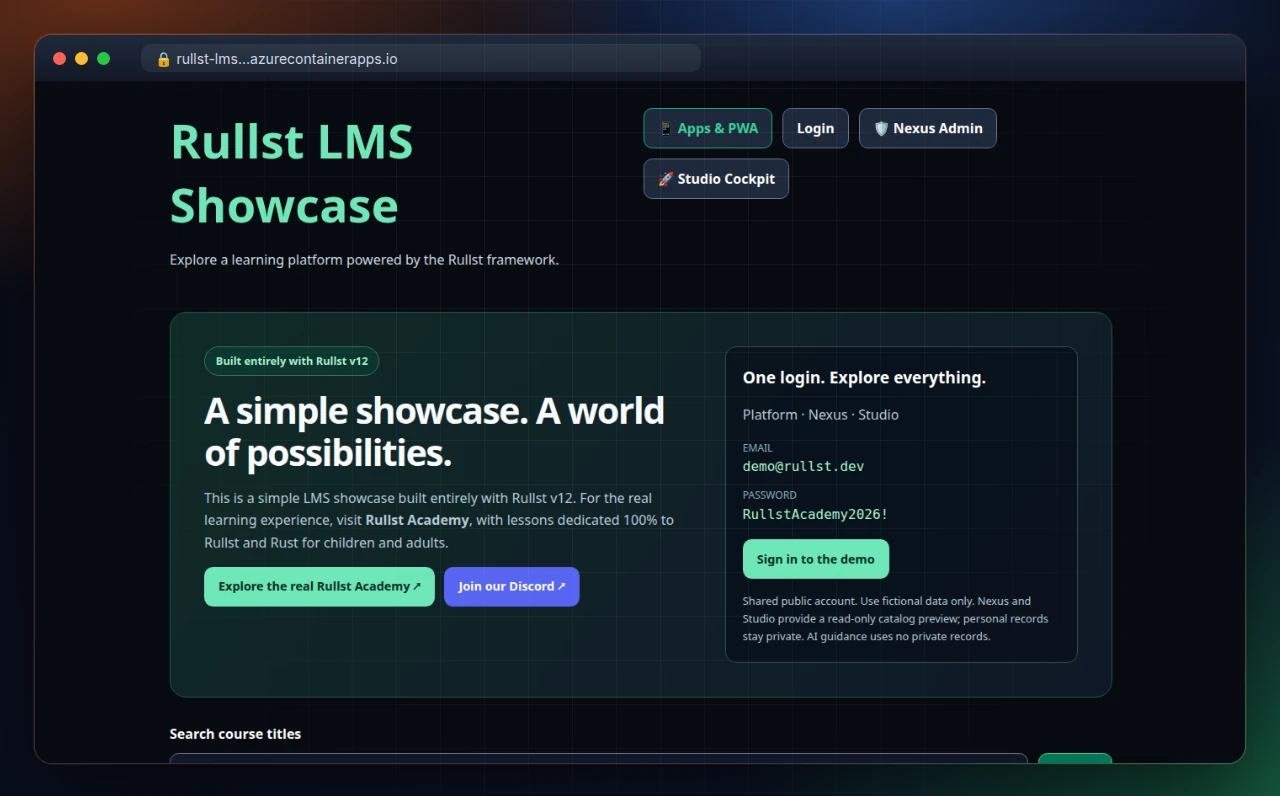
🎓 LMS — course catalog and learning platform · Open ↗ |
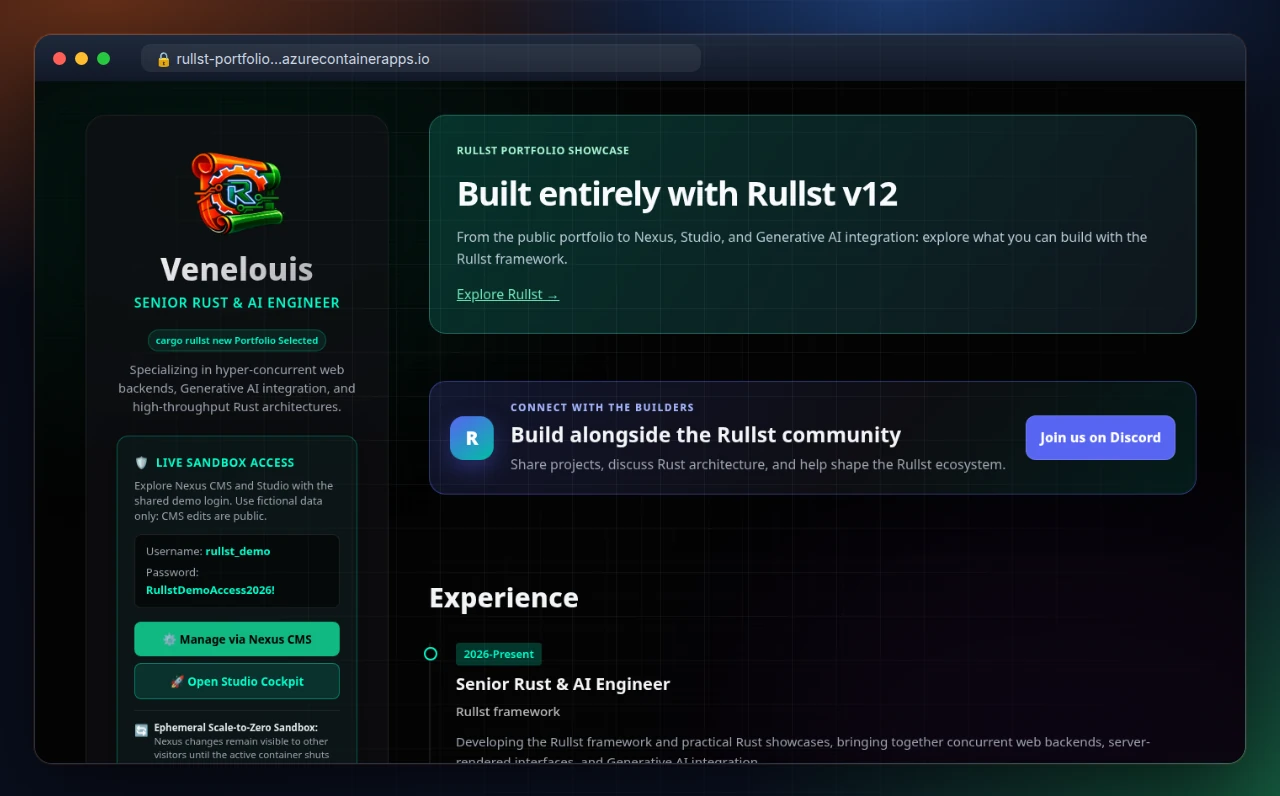
💼 Portfolio — projects, experience, Nexus and Studio · Open ↗ |
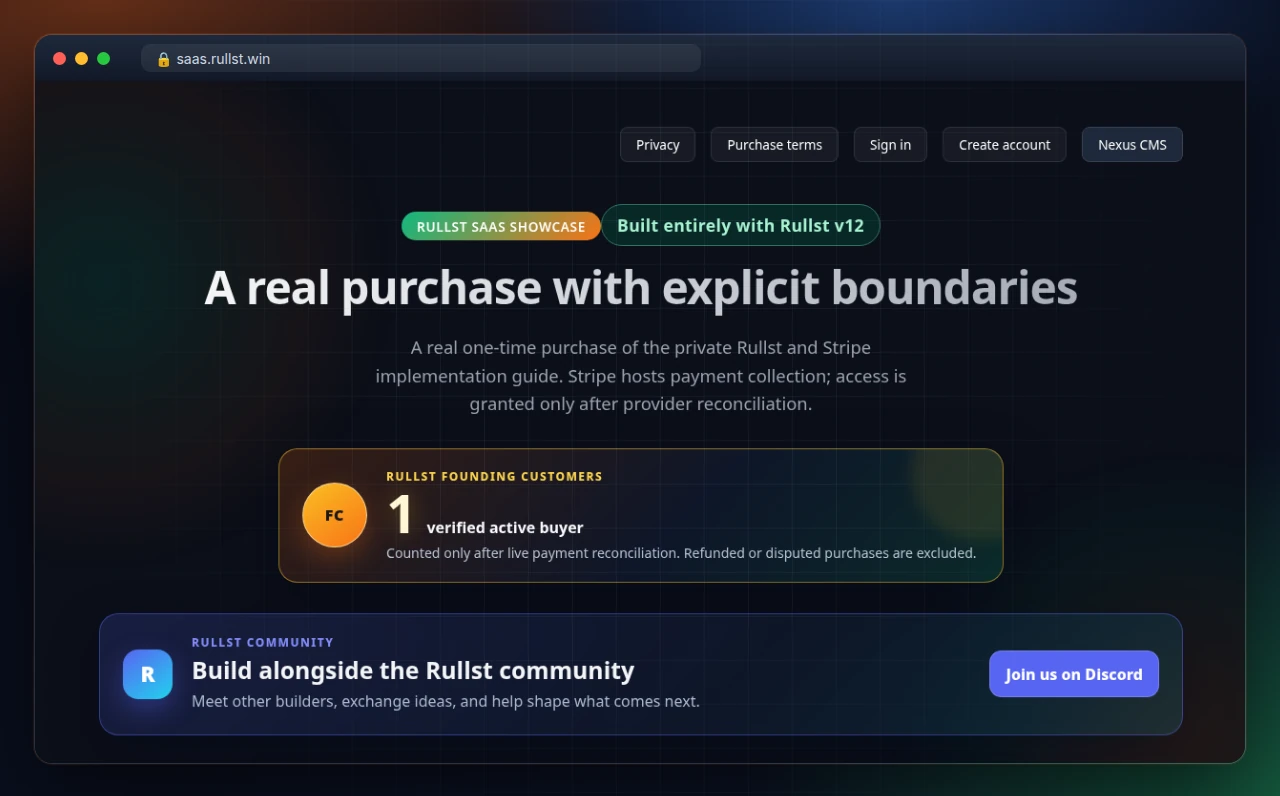
🛒 SaaS in production — real purchases with Stripe · Open ↗ |
The demos scale to zero when idle, so the first visit can take a few seconds to wake up — that is hosting startup, not Rullst's request time. The SaaS checkout is live and charges real money; the Showcase payment demos are not.
Prefer to run something locally? The reproducible SaaS example uses the v13 CLI from this checkout on Linux and covers generation, login and tenant-scoped notes on a disposable SQLite database, and the WebGPU wave example serves browser graphics from Rullst.
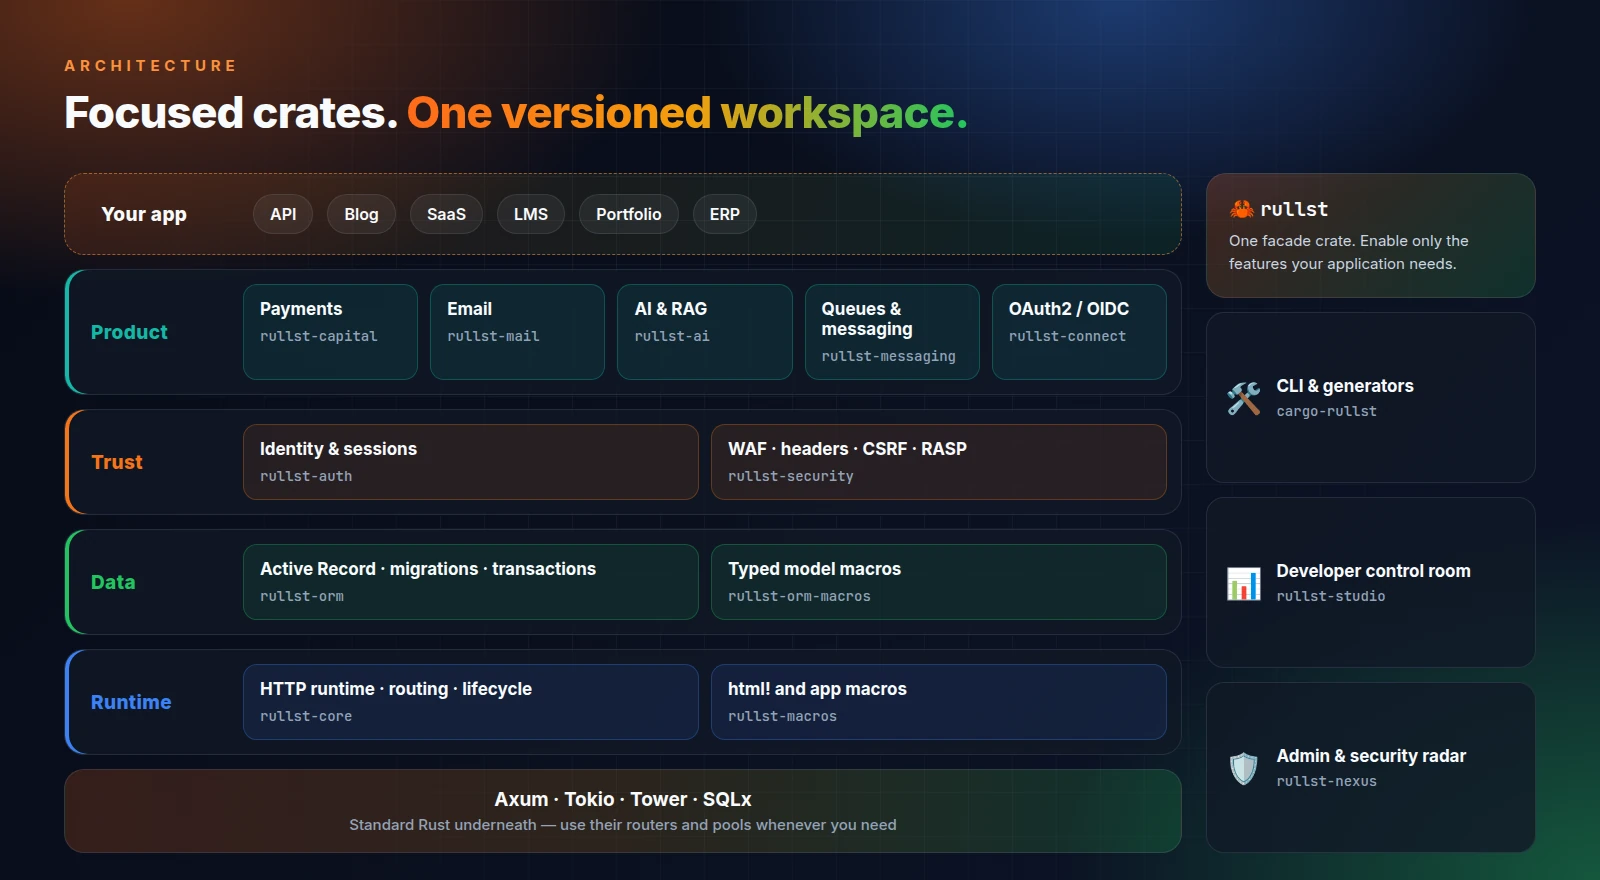
Rullst is a family of focused crates in one versioned workspace — select only what your application needs. The stable v12 release publishes sixteen crates; detailed feature and provider boundaries live in the specification. In v13, every crate is labelled Core, Extension or Experimental; see the maturity tiers.
Browse the crate directory
| Crate | Focus | Tier |
|---|---|---|
| rullst | Public framework facade and feature selection | Core |
| rullst-core | HTTP runtime, routing, lifecycle and telemetry | Core |
| rullst-orm | Relational models, transactions and capability-specific persistence | Core |
| rullst-auth | Passwords, sessions, passkeys and authorization helpers | Extension |
| rullst-security | Defense-in-depth middleware, guards and audit helpers | Core |
| rullst-connect | OAuth2/OIDC identity integrations | Extension |
| rullst-ai | Guarded local/cloud clients and tenant-aware retrieval | Extension |
| rullst-capital | Billing contracts, Stripe and experimental InfinitePay adapters, webhooks | Extension |
| rullst-mail | Transactional email with Resend, AWS SES, SendPulse and SMTP transports, and delivery controls | Extension |
| rullst-messaging | Broker-neutral contracts and durable local messaging | Extension |
| rullst-studio | Local developer control room | Extension |
| rullst-nexus | Registered-model admin with explicit access policy | Extension |
| rullst-iot | Bounded no_std helpers and signed OTA verification, not device integration | Experimental |
| rullst-macros | Compile-time HTML and application macros | Core |
| rullst-orm-macros | Typed ORM code generation | Core |
| cargo-rullst | Project scaffolding, development and upgrade CLI | Core |
The v13 workspace on main also contains unpublished candidates, all in the
Experimental tier:
rullst-privacy,
rullst-supervision,
rullst-media and
rullst-labs are in
the v13 release order.
Tiers (v13): Core packages are needed by every application. Extensions are optional and supported. Experimental packages are optional, may change between 13.x releases and are not validated in every scenario. Experimental does not mean broken. The maturity tiers page defines each promise and labels the CLI generators.
Rullst Academy is a free learning platform — built with Rullst — where you can learn Rust, Rullst, Git/GitHub, web development, databases and more through short lessons and practical projects, in Portuguese, English or Spanish.
Start learning at Rullst Academy ↗
Rullst is maintained with the rigor you expect from security software:
- No panics in production code, enforced by CI across the published runtime crates.
- No new
unsafeoutside a reviewed OS/FFI allowlist. - At least 90% line coverage, enforced, plus fuzzing, property tests, sanitizers and Kani/Miri checks on selected critical code.
- Supply-chain hygiene: RustSec and license policy on every change, SHA-pinned Actions, and an SBOM with build-provenance attestation for every release.
- A fast Linux gate on every pull request, with the complete Linux/macOS/Windows matrix every night and before every release.
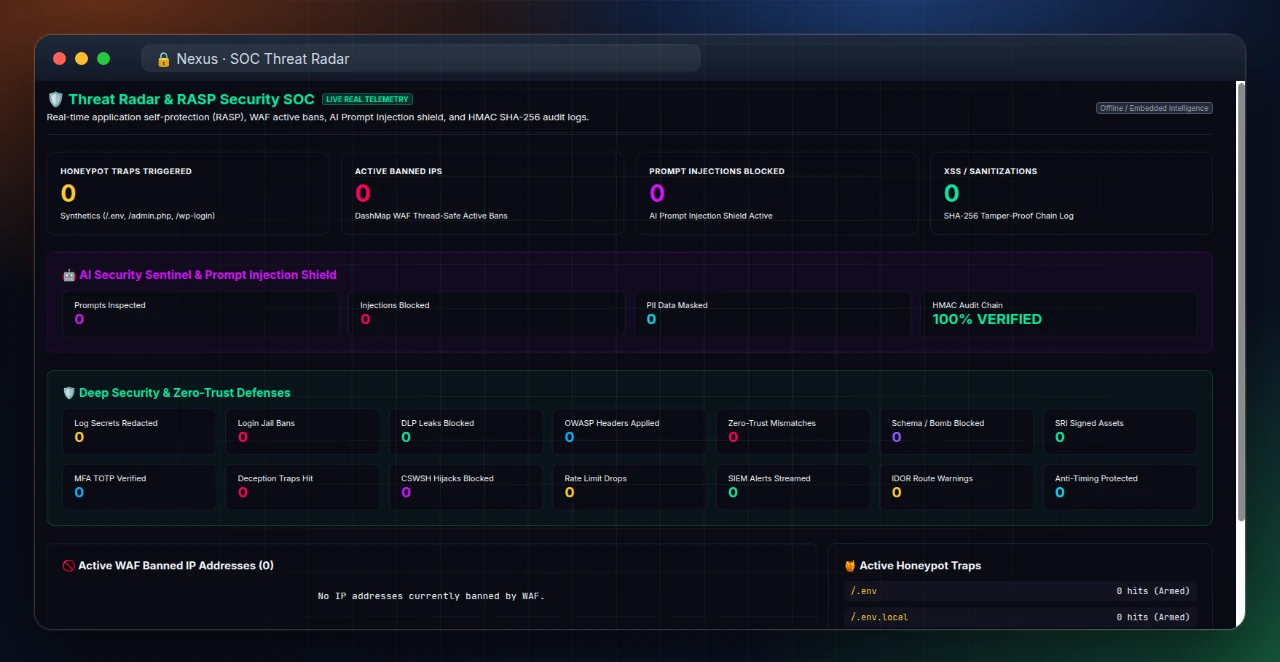
The Nexus security radar (recorded screenshot).
These results are evidence for their stated scope, not a security certification of every application built with Rullst. Explore the release audit, capability status and quality scorecard.
🛡️ Open the verification dashboard (39 workflows)
Badges are pinned to the main branch; they report the latest matching run, not a certification or deployment guarantee.
| Continuous or change-aware gate | Development main status |
Actual scope |
|---|---|---|
| Rust CI |  |
Format, all-target/all-feature Clippy, a Linux gate on pull requests, every Linux shard after merge and the complete Linux/macOS/Windows matrix nightly; Cargo-aware doctests sourced from all 51 tutorial pages, strict DB boundaries, feature boundaries, generated-code checks, and MSRV 1.96.0. |
| Declared MSRV |  |
Every publishable manifest declares Rust 1.96.0 and CI runs an explicit workspace all-feature check with that toolchain. |
| GitHub Actions lint |  |
Validates workflow syntax, expressions, embedded shell, and full-SHA third-party Action pins. |
| Documentation |  |
Builds the mdBook and rejects broken local links and anchors; scheduled/manual runs also preserve an informational external-link report. |
| End-to-end smoke |  |
Boots the release blog example and verifies HTTP, security headers, form flow, and SQLite persistence. |
| Codecov — whole repository | |
The badge reports the current branch aggregate. The stable-source LLVM run at eb11f892 measured 90.3220% (79,813/88,365 lines) before Codecov upload. The enforced repository floor is ≥90% with zero tolerance. |
| Codecov — framework libraries |  |
Runtime libraries are enforced separately at ≥90%. CLI and proc-macro components stay separately visible; Coverage CI uploads their real LCOV evidence with OIDC. |
| Cargo Audit |  |
RustSec advisory scan with only governed, expiring exceptions; the daily run also audits the stable v12 locks. |
| Security exception governance |  |
Cross-checks scanner allowlists against the owner/expiry ledger, then independently reruns Cargo Audit. |
| Cargo Deny |  |
Advisory, license, ban, and source policy. |
| CodeQL SAST |  |
Rust semantic analysis after an all-target/all-feature build. |
| OpenSSF Scorecard |  |
The badge renders the score from the official public Scorecard JSON report; the pinned Scorecard workflow publishes OIDC-authenticated results on each main push and weekly. A score is evidence, not a security certification. Evidence and improvements. |
| Cargo Machete |  |
Unused direct dependency detection. |
| SemVer checks |  |
Supported library APIs are compared with exact latest non-yanked registry baselines; never-published packages and unsupported proc-macro/binary surfaces are reported explicitly. |
| Zero-panics policy |  |
Denies panic-family operations in published production targets and generated runtime templates. |
| Unsafe boundary |  |
Denies new production unsafe code outside the reviewed OS/FFI allowlist. |
| Secret scanning |  |
Verified-secret scan across the configured Git history range. |
| Spellcheck |  |
Repository-wide typo detection. |
| Crate architecture policy |  |
Compares the real publishable-crate dependency graph with a versioned, reviewed repository policy. |
| WebAssembly matrix |  |
Compiles Core, the public facade and macros for browser Wasm and WASI Preview 1. |
Bare-metal no_std matrix |
 |
Builds IoT helpers for Cortex-M and RISC-V targets; this is compile evidence, not hardware testing. |
| IoT integration |  |
Host tests, signed OTA invariants, and a Cortex-M build. |
| IoT crypto containment |  |
Path-aware signed OTA, Vault, advisory, and simulator-boundary checks; no PQC/HSM certification claim. |
| Omni desktop matrix |  |
Generates fresh web shells and checks their Tauri crates on Linux, macOS and Windows; no installer, signing or store claim. |
| Omni Android compile |  |
Generates a fresh shell and compiles an unsigned Android debug APK; no physical-device, Play testing/signing or store claim. |
| Omni iOS simulator |  |
Path-aware fresh scaffold generation and compilation on a macOS iOS simulator target; no device, signing or App Store claim. |
| PR security evidence |  |
Pull-request-only bounded IDOR/RBAC heuristics and CycloneDX SBOM artifact. It intentionally has no continuous main status. |
Deep or irreversible workflows are intentionally not presented as continuously green main gates:
| Deep evidence | Trigger and enforcement |
|---|---|
| Benchmark regression | Weekly, main push, or manual; eight published groups backed by nine Criterion benchmark binaries emit non-blocking alerts at a 20% regression. |
| Property testing | Weekly/manual release-mode invariant testing with 10,000 configured cases. |
| TSan and ASan | Daily/manual package matrices on a pinned verifier-only nightly. |
| Fuzzing / corpus minimization | Forty-two manual libFuzzer jobs; weekly/manual corpus maintenance is informational. |
| OWASP ZAP | Manual baseline over three release surfaces: generated REST API and LMS starter are blocking with no ignored alerts; the deliberately CDN-backed blog showcase remains an explicitly informational boundary. |
| Kani, Miri, mutation testing, cargo-udeps | Manual or scheduled research signals: selected Kani/Miri scopes are strict, while mutation and unused-dependency findings remain explicitly informational. |
| v13 Verus pilot | Optional production-linked age-policy proof with pinned tooling and three negative controls. Hosted registration/acceptance remains pending; no framework-wide correctness claim. |
| GitHub Pages | Deploys development documentation from main; it is not a code-quality gate. |
| Release and provenance | Exact version tags only: full verification, package-all, evidence bundle, checksums, GitHub build-provenance attestation, changelog-derived release notes, and ordered crates.io publication. This does not claim a project-wide SLSA level or independent certification. |
Scheduled events use the repository's default branch, so scheduled and
continuous development evidence refer to main; stable v12 has its own branch.
The branch-protection profiles and the exact scope of all
39 workflow definitions in this source branch are documented in
WORKFLOWS.md.
📖 Read the detailed breakdown of all CI/CD and security workflows.
🧭 Capability Status & Vision Decisions preserves ambitious features that are partial or not implemented, with an explicit recommendation and rationale for each one.
📋 Simple Capability Status and the per-commit quality scorecard keep feature progress separate from SHA-bound engineering evidence.
From an existing application's root:
cargo rullst upgrade --dry-run
cargo rullst upgrade
The CLI coordinates dependency updates, backs up controlled files and runs compiler checks. Review the plan and your application's behavior; it does not migrate production data. Assisted upgrade tutorial · v5 → v12 migration guide
This main branch is where v13 is being built (13.0.0-alpha.1). The
commands above install the stable v12 line, maintained on the
v12 branch; v5 is no longer maintained.
In development for v13: email login and scoped API tokens, active-session
management with remote logout, private S3/R2 storage with resumable uploads,
durable outgoing webhooks and recurring jobs, Redis Streams messaging,
distributed tracing, a recoverable Live UI, cargo rullst ai, a terminal
assistant that proposes reviewed changes to your project, a cargo rullst new
wizard that previews the files and commands before writing anything
(--dry-run without prompts) and cargo rullst tour, a guided walkthrough of
the main commands. The v13 CLI also adds live request metrics to
cargo rullst dash; toolchain, project, configuration, database, migration,
security and disk checks with fixes and --json to cargo rullst doctor; a
searchable command list on the cargo rullst home screen;
cargo rullst completions <shell> for tab completion; v12 → v13 source
findings to cargo rullst upgrade; and cargo rullst audit --report, a
Markdown, HTML or JSON security evidence report mapped to OWASP ASVS 5.0
Level 1, with a personal-data inventory and accessibility checks
(guide). It is
evidence for a reviewer, not a certification. cargo rullst footprint runs a
bounded local load and reports requests/s, latency, CPU time, memory, sizes and
energy where the machine exposes it, each with its method
(guide).
cargo rullst add <capability> enables mail, auth, AI, Nexus or Studio in an
existing project (feature, .env.example placeholders and the code to paste;
--dry-run shows the diff), and cargo rullst new initializes a Git
repository (--vcs none skips it). Until v13 is released, these are
development candidates, not shipped features.
v13 roadmap · v13 adoption guide · Compatibility policy · v12 release record
The benchmark hub publishes eight Criterion groups backed by nine benchmark binaries. They measure specific workloads and regressions — not universal speed or a ranking of frameworks. Read the methodology alongside the results.
Try a blueprint, report a reproducible bug, improve a tutorial or contribute a focused change with tests. Documentation, accessibility and integration feedback matter as much as new features.
Contributing · Issues · Discord · Community links · Our story and philosophy
⭐ If Rullst sparks your curiosity, a star helps more developers discover it.
MIT license · Report a vulnerability privately · Website privacy notice
All glory and honor to God יהוה in the name of Yeshua the Messiah (Jesus Christ).
