


Jon “GainSec” Gaines is a hacker, cybersecurity leader, offensive security engineer, and an independent security & vulnerability researcher.


All work and projects on this GitHub are his own. Created using his own resources and time. They do not reflect any past or previous employer or client.


- Flock Safety Security Vulnerabilities: Examining the Security Posture of an Anti-Crime Ecosystem is a versioned whitepaper and disclosure archive covering >50 vulnerabilities I found in Flock Safety's gunshot detection, license-plate reader, and compute hardware, with defender guidance and repository-maintained finding/CVE accounting.
- Flock Safety Offensive Security Tooling: BirdShot is an offline-first offensive framework for authorized Flock Safety security assessments and penetration testing; Trap Shooter / Sniffer / Alarm detects nearby Flock-related Wi-Fi activity; and the Falcon/Sparrow EDL firehose provides EDL-mode interaction tooling for researched ALPR hardware.
- Verkada Security Vulnerabilities: Verkracked is an ongoing independent security research project examining owned Verkada hardware. Public releases currently include a local cloud framework for Verkada alarm hubs, a Sub-GHz interoperability framework, a CB62 local cloud emulator, VerkEye—an evidence-first local runtime for an owner-extracted CB62 vision model—and read-only firmware-acquisition tooling for owned or explicitly authorized CB62 hardware. Parts 1–3 are scheduled for public disclosure on December 5, 2026.
- Digital Ally / Uniview: the ThermoVu / Uniview security research is accompanied by the Uniview LAPI Research Toolkit, ONVIF enumeration, and the TensorFlow generic harness used for OEM-style model-pipeline replay.
- Connected infrastructure: Tridium Niagara CVE PoCs preserve proofs of concept for CVE-2017-16744 and CVE-2017-16748.
- Vehicle and V2X material: Phrack 72 V2X companion artifacts preserve raw output and logs accompanying my paper that was published in Phrack 72.

- macOS Printer Simulator Security Research — Public disclosure documenting three validated technical weaknesses with reproduction source, evidence, current Low/Low/Informational ratings, and Apple’s recorded disposition.
- AutoPro / Mayton CarPlay adapter research — Public wireless CarPlay adapter analysis, findings, evidence, source tools, and the first C2 for aftermarket Android Auto / Apple CarPlay dongles.
- AOL Desktop Gold Security Research — Independent group security research release covering a handful of vulnerabilities found in AOL Desktop Gold.
- Little Tikes Dream Machine reverse engineering — Notes and material from reverse engineering the Little Tikes Dream Machine.


The following incomplete list extends the GitHub record with security research, vulnerability disclosures, technical walkthroughs, leadership writing, papers, talks, and media published on GainSec.com or in external publications.
SectorGov: SectorGov is a no-account public directory for discovering government service links by location, service, vendor, and software. The accompanying article documented 7,373 service links when Government Run OSINT Services was published.


|
|
|
|
|
|
|
|
|
|
|
|
| Persistent research loops for source code, binaries, and evidence: specialist agents share a workbench that tracks coverage, scoped authority, findings, and the evidence behind each conclusion. | Model-driven vulnerability hunts over firmware and source code, with bounded jobs, a hash-chained ledger, and findings promoted only when independently reproduced. |










- anti-crime-ecosystem-research — Formal whitepaper, defender material, and disclosure archive for Flock Safety's hardware ecosystem.
- BirdShot — An offline-first offensive framework for authorized Flock Safety security assessments and penetration testing.
- Flock-Safety-Trap-Shooter-Sniffer-Alarm — ESP32-C6 firmware that detects and alerts on nearby Flock-related Wi-Fi activity.
- onvif-enum — Read-focused ONVIF enumeration for cameras, NVRs, and OEM physical-security devices.
- Uniview-LAPI-Research-Toolkit — Conservative Uniview/OEM LAPI client with profiles and explicit write controls.
- DigitalAlly-ThermoVu-Uniview-Security-Research — Research archive for a facial-recognition and thermal access-control terminal.
- verkada-verkracked-alarm-hub-local-framework — Local cloud emulator and owner-controlled laboratory framework for operating Verkada BH-series wireless alarm hubs without the vendor cloud.
- verkada-verkracked-subghz-framework — Sub-GHz interoperability framework for decoding, generating, replaying, and correlating Verkada alarm-hub wireless protocol traffic in authorized labs.
- CVE-2017-16744-and-CVE-2017-16748-Tridium-Niagara — Proofs of concept for CVE-2017-16744 and CVE-2017-16748 in Tridium Niagara.
- flock-safety-falcon-sparrow-alpr-edl-firehose — EDL-mode interaction tooling for Flock Safety Falcon/Sparrow ALPR hardware.
- verkada-verkracked-bullet-cam-cloud-emulator — Owner-controlled local cloud emulator for lawfully owned Verkada CB62 cameras, with bounded enrollment, artifacts, and relays.
- VerkEye — Evidence-first local runtime for inspecting and executing an owner-extracted Verkada CB62 vision model on macOS and Linux.
- verkada-verkracked-ambrella-CB62-firmwaredumper — Read-only firmware acquisition and recovery-evidence tooling for lawfully owned or explicitly authorized Verkada CB62 hardware.

- macos-printer-simulator-security-research — Full disclosure and reproduction archive documenting three technical weaknesses in Apple's Printer Simulator.
- AOL-Desktop-Gold-Security-Research — Independent group security research release covering a handful of vulnerabilities found in AOL Desktop Gold.

- 3rdParty-Carplay-AndroidAuto-Dongle-Security-Research — Public Mayton/AutoPro wireless CarPlay adapter analysis, findings, evidence, source tools, and the first C2 for aftermarket Android Auto / Apple CarPlay dongles.
- Wireless-Attack-Vectors-Against-Automobiles — Published whitepaper surveying wireless attack vectors against automobiles.

- Little-Tikes-DreamProjector-Reverse-Engineering — Notes and material from reverse engineering the Little Tikes Dream Machine.

- Phrack-72-Raw-Output-V2X — Raw output, logs, and companion artifacts for GainSec's V2X paper in Phrack 72.


- Qwen 3.6 Tool-Call Fix — Configuration fix for Qwen 3.6 tool calls on DGX Spark with LM Studio and OpenClaw.
- M5NanoC6-Zigbee-Sniffer — M5Stack M5NanoC6 Zigbee sniffer build instructions.
- CloudGoatTutorial — CloudGoat lab setup tutorial using Windows, VirtualBox, and Ubuntu Server.

- Silk-Road-Lecture — Lecture material preserved in the GainSec project archive.

- n8n-workflow-whisper-server — n8n workflow connecting uploaded audio to a Whisper transcription server.


- DWARF — Cardano and Amaru fuzzing and adversarial-testing framework for serialization, protocol, runtime, resource, and consensus surfaces.
- DWARF-Freeze — Interactive Cardano node debugger for holding, inspecting, editing, forwarding, or dropping events; an add-on to DWARF.

- crt.sh-OSX — macOS-compatible passive certificate transparency enumeration script.

- LeakScope — Self-hosted exposure investigation with Shodan, ZoomEye, Netlas, evidence capture, monitoring, and visual workflows.
- Dorker — CLI and web app for formatting search-engine dorks.
- FOSINT — Free and open-source intelligence resource index.
- Base-Google-Dorks — A basic, explicitly incomplete collection of Google dorks.

- GoldenNuggets-1 — Burp Suite extension for creating wordlists from site-map paths and parameters.
- TreeHouse-Wordlists — Wordlists for authorized penetration testing and vulnerability assessment.
- Hackers-LunchBox — Attack and finding maps for penetration tests, bug bounties, and red-team work.
- Mac-OSX-Application-Fingerprint-And-Security-Tool — Automates baseline checks for macOS application security assessments.
- Quick-Engagement-Directory-Maker — Creates repeatable engagement directory structures for security assessments.

- gainsec-in-the-middle — On-demand MiTM router/access point for authorized embedded and IoT assessments.
- GITM-CardputorZero — CardputerZero wireless research AP with Ethernet WAN, packet capture, traffic inspection, Android CA preparation, and Burp exports.
- Weaponized-Mousejack-Keysniff — Research tooling built around the MouseJack and KeySniffer vulnerabilities.

- RTLOify — Creates RTLO strings and filenames for controlled bypass testing.

- vncpwn — Legacy Python security tool retained in the public archive.
- LeakLooker-X---2022 — Archived 2022 working snapshot of LeakLooker-X.


- AutoProber — Agent-driven flying-probe automation with microscope mapping, CNC motion, review gates, and independent safety monitoring.
- ZeroProbe — CardputerZero GPIO, UART, and I²C explorer with guarded signal operations, VCD capture, logging, and a web dashboard.
- RapidPower-RoboDog — Clean-room Python BLE control library and local web dashboard for a consumer robot dog.
- Super-Awesome-AI-Driver — Reverse-engineered camera-car dashboard and agent API with video, audio, and motion control.

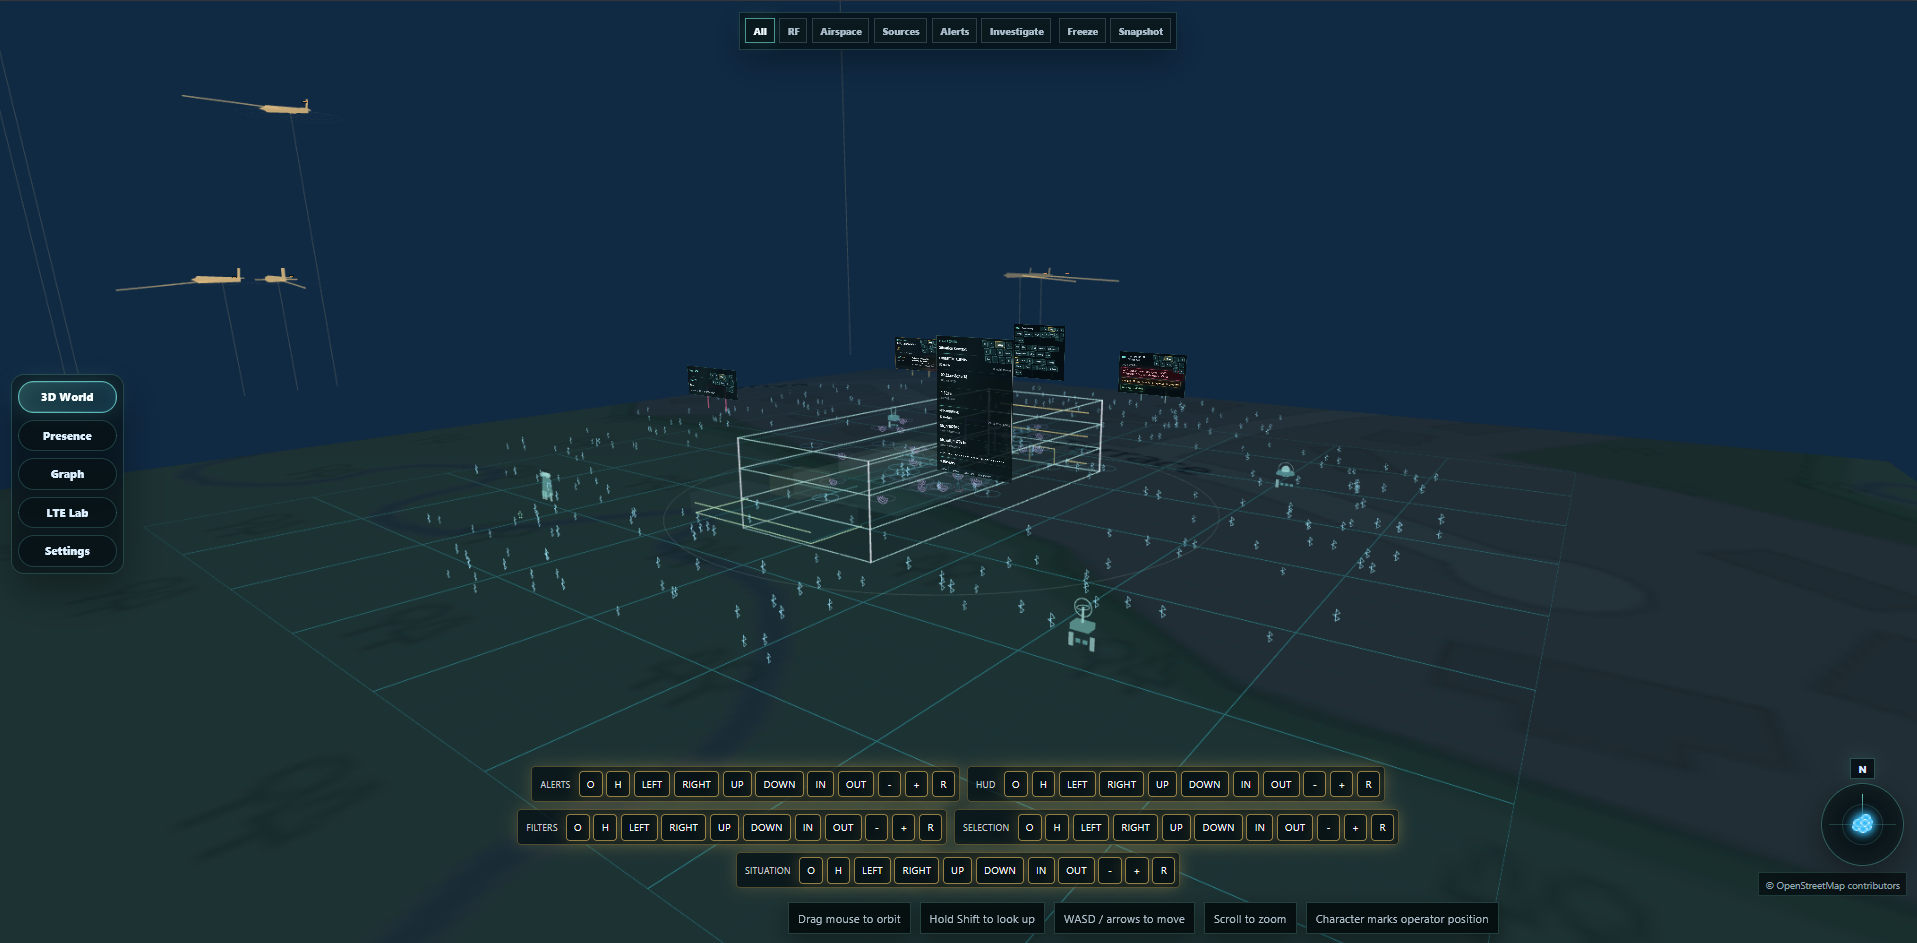
- Tree-House-Defense-System-TDS — Self-hosted 3D/XR RF awareness with Steam Frame WebXR across Wi-Fi, BLE, ADS-B, rail, IoT, and LTE lab data.
- M5Stack-Core2-PaxCounter-WiFi-Bluetooth-Monitor — Nearby Wi-Fi and Bluetooth population monitor for M5Stack Core2.

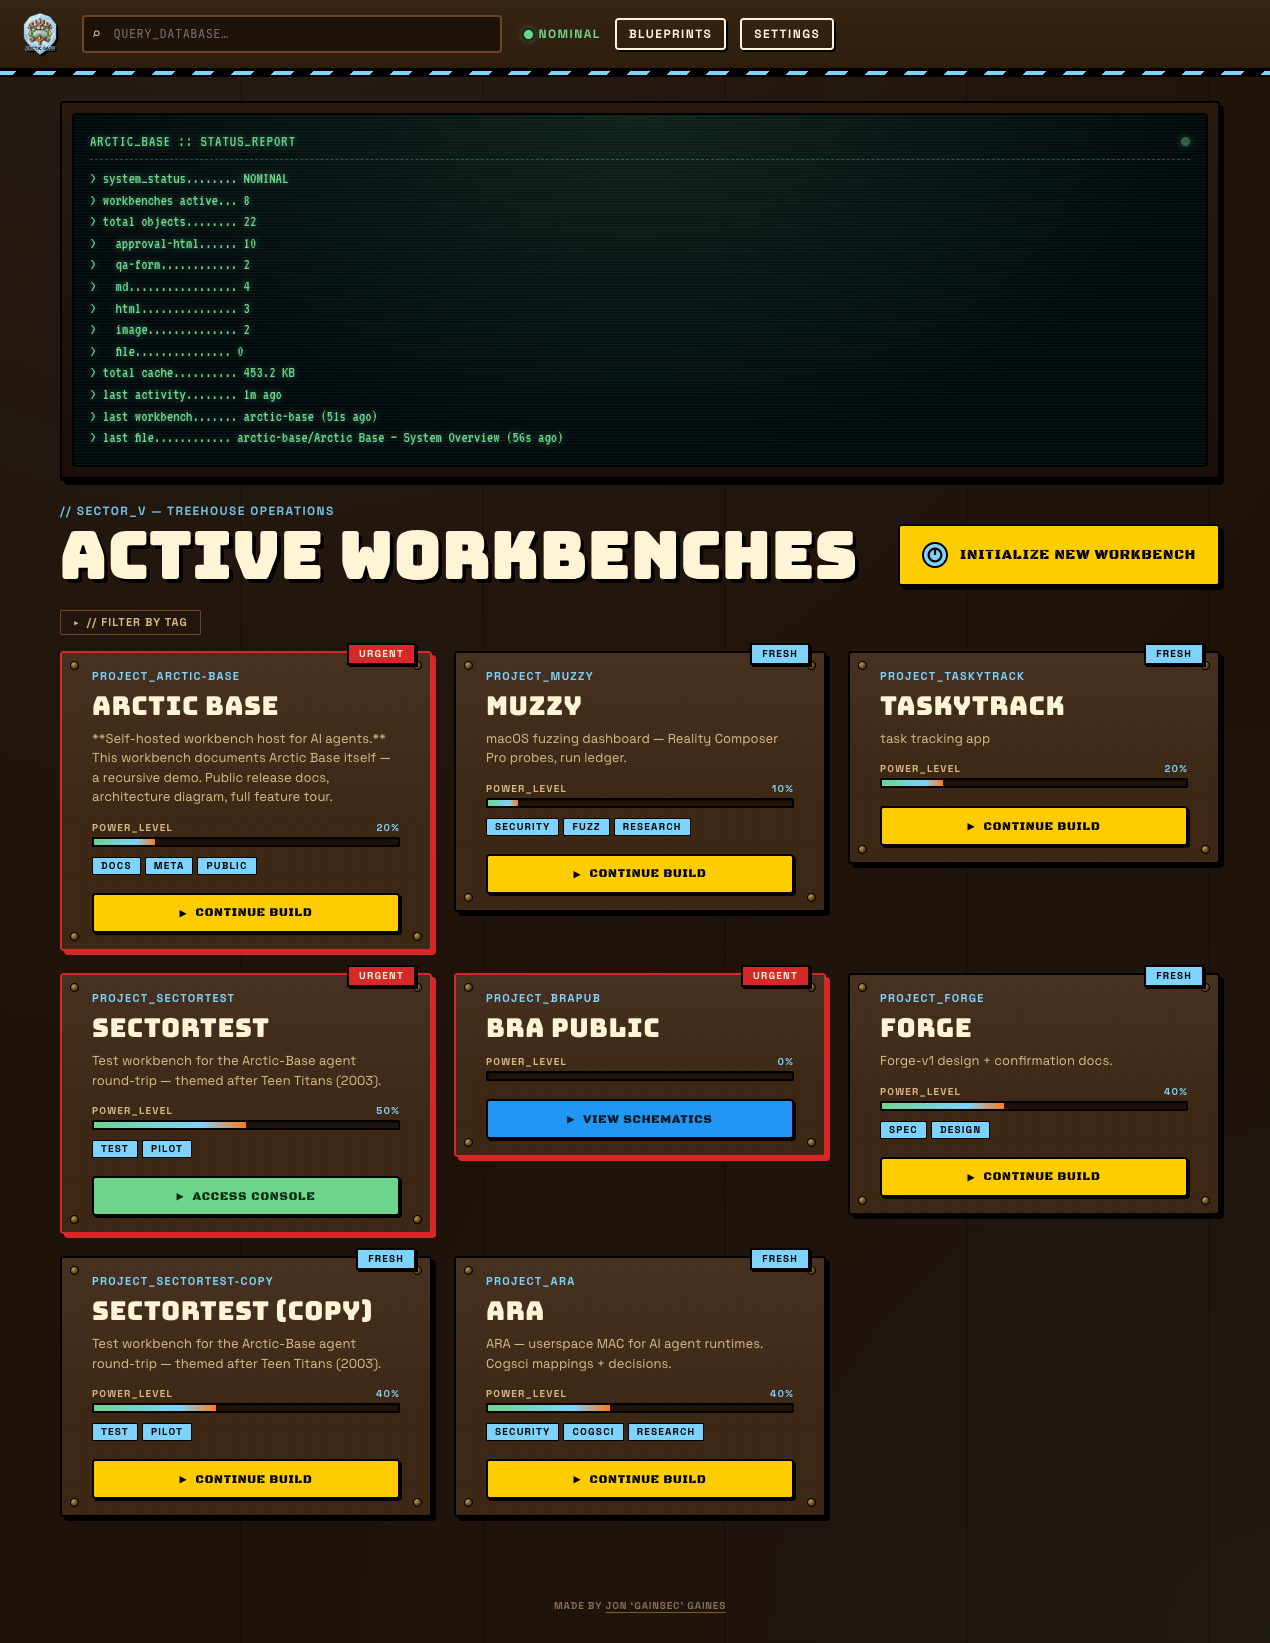
- ArcticBase — Self-hosted, auditable workbench for agent approvals, runbooks, files, and review artifacts.
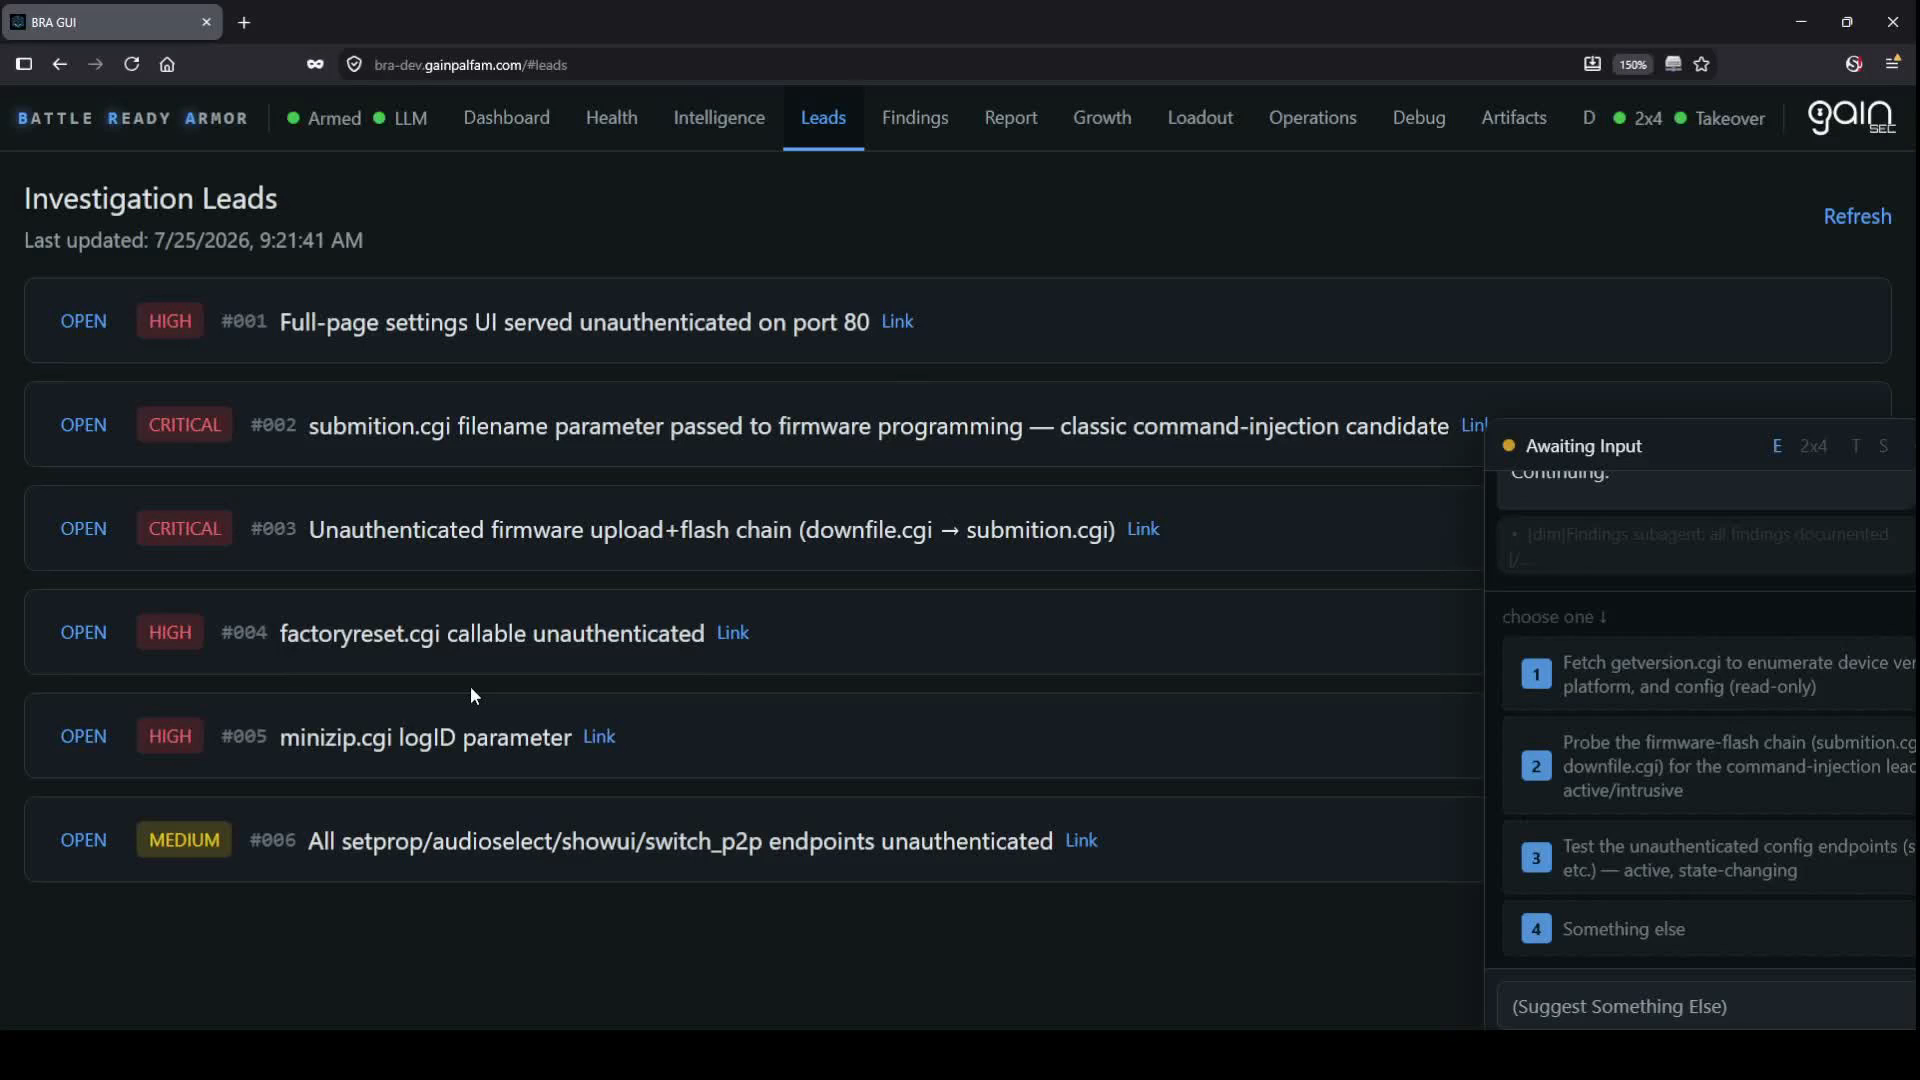
- ReadyArmor-Battle-Ready-Armor-BRA — Operator-led AI security assessment with host-native controls, privacy mappings, evidence, reporting, and reusable methods.
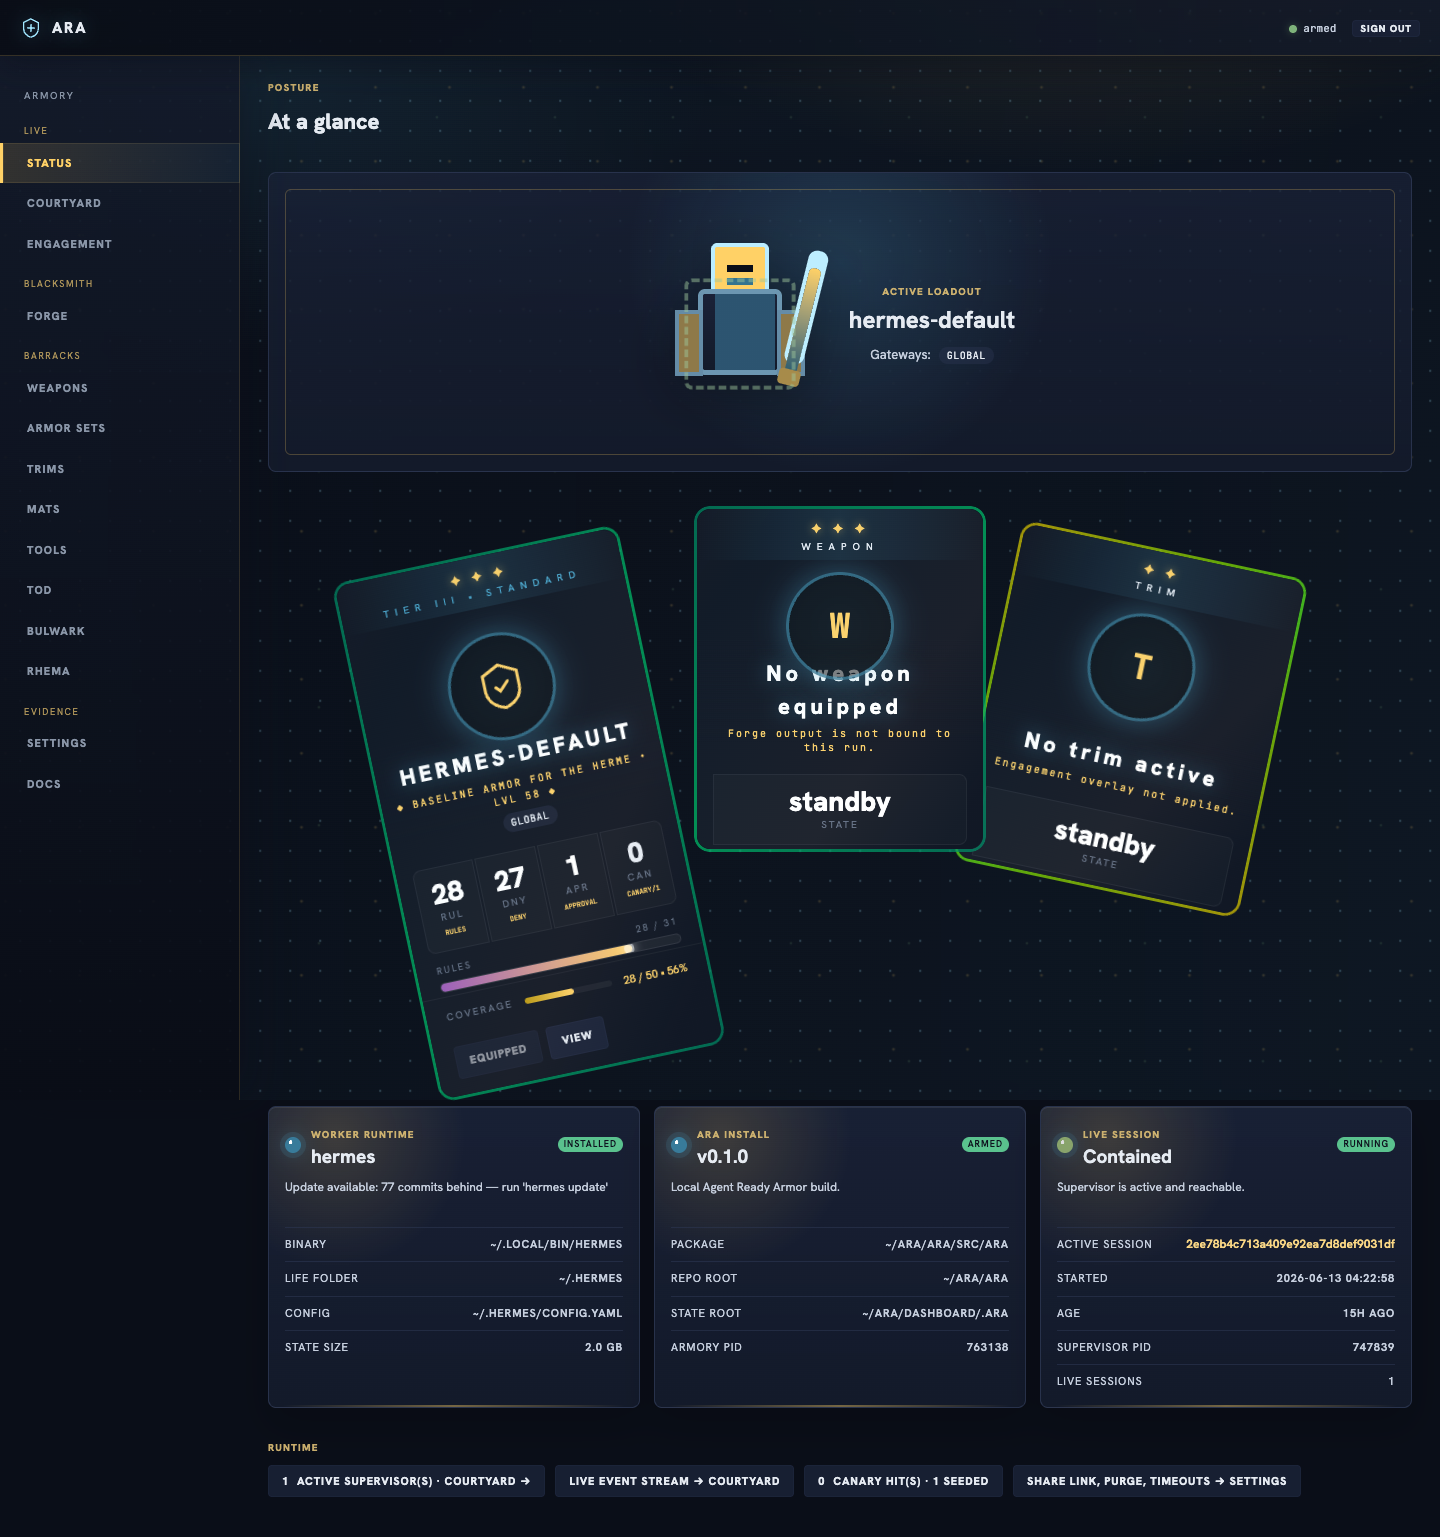
- ReadyArmor-Agent-Ready-Armor-ARA — Supervised host-native agent work with reusable methods, independent operation controls, source records, and evidence review.
- ReadyArmor-Reverse-Engineer-For-All-REFALL — Persistent source and binary research with specialist agents, coverage tracking, scoped authority, and an evidence ledger.
- ReadyArmor-DeepSeaResearch-DSR — Model-driven firmware and source research with bounded jobs, a hash-chained ledger, and independently verified findings.
- BattleReadyArmor-Slim — Governed AI-augmented security assessment framework where the operator retains authority.
- battlereadyarmor-pilot — Controlled command interface for directing offensive-security workflows.
- MacOS-ImagePlayground-Improved — macOS experimentation app for Apple's Image Playground API.
- AgentReadyArmor-Teaser — Preview of a control-in-depth runtime substrate for autonomous agents.
- tensorflow-generic-harness — Replay harness for OEM-style YOLO/SSD TensorFlow Lite model pipelines.
- BattleReadyArmor-PublicPreview — Public architecture preview for governed, privacy-preserving agentic assessments.
- GainSec-Local-AI-Stack — Scripts, workflows, and notes from local AI-stack prototyping.
- MacOS-AppleIntelligence-Harness — Local macOS harness for prompts, pipelines, and consistency experiments with Apple Foundation Models.
- RealHermes — Experimental spatial Hermes Agent companion for desktop and WebXR with voice, headset-view vision, and movable document panels.

- PineapplePager-Themer — Visual theme editor and exporter for the Hak5 WiFi Pineapple Pager.
- Homarr-Integrations-Widgets — Independent Homarr integrations and widgets for infrastructure, local AI tooling, service health, usage data, and dashboard operations.
- unicode-secret-message — Small interface built during research into RTLO, PDF, and other Unicode characters.

- SectorMap — Offline-first self-hosted dataset browser with a galaxy-style archive interface.


- IG-Clone-Tracker — Instagram clone for lab research, prototyping, and tracking experiments.
Caution
This archive contains dual-use security research and tools. Use them only in owned or explicitly authorized environments, and follow each project’s safety and disclosure boundaries.
