


ASC-IT is a French cybersecurity and software engineering company. We run offensive security assessments (web, Active Directory, cloud, Kubernetes, IoT) for companies that want continuous, evidence-based security, and we build Darkmoon: the open-source platform that runs a full penetration test on its own, and never lets the AI see your real data.
Important
License change. Darkmoon Community is moving from the GNU GPL v3.0 to the GNU AGPL v3.0. Every commit published up to edfe9cb (27 October 2026) stays under the GNU GPL v3.0, and the contributions made by outside contributors before the switch also stay under the GNU GPL v3.0 (they are not relicensed). Details: LICENSING.md.



Point Darkmoon at a target you are authorized to test. 50 specialist AI agents reason, chain real exploits across web, APIs, Active Directory, Kubernetes, cloud (AWS, Azure, GCP), CI/CD, databases, IoT firmware and AI/LLM endpoints (OWASP LLM Top 10), and return proof for every finding: the exact command, the raw output, reproducible. Self-hosted, AGPLv3, and thanks to the Privacy Gateway the model only ever sees IP_PRIVATE_001, never your real IPs, hosts or credentials.
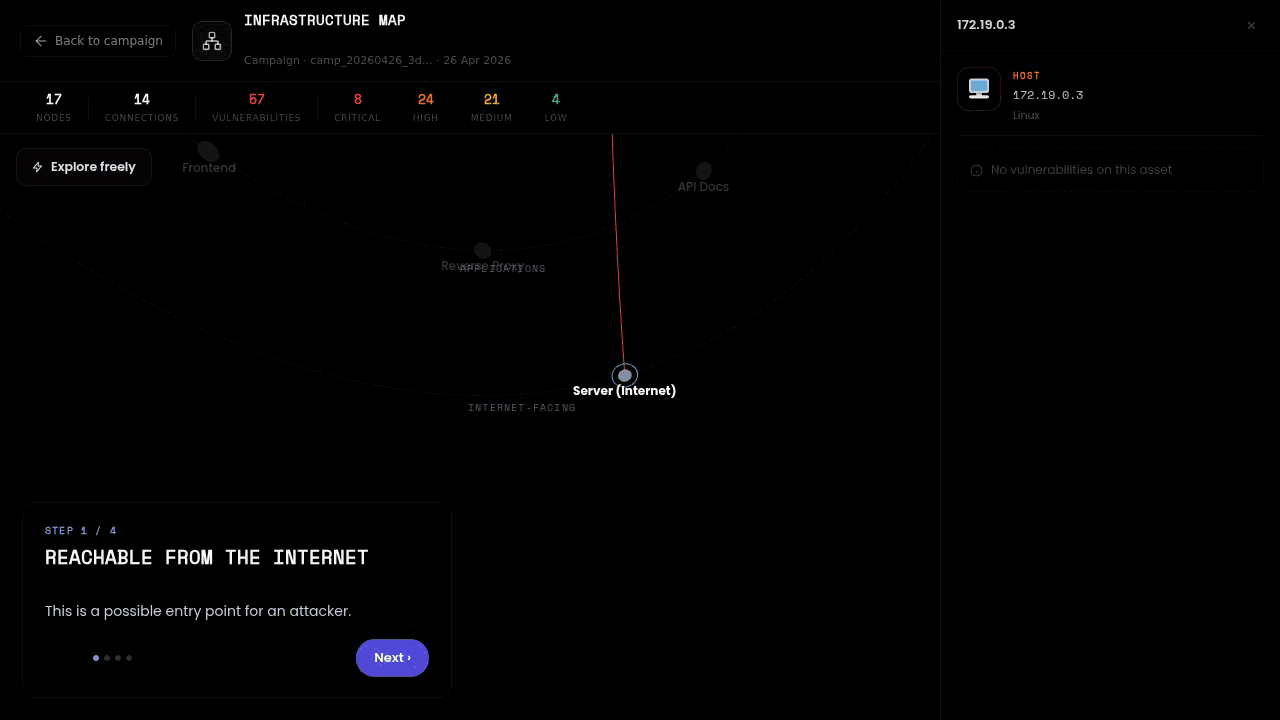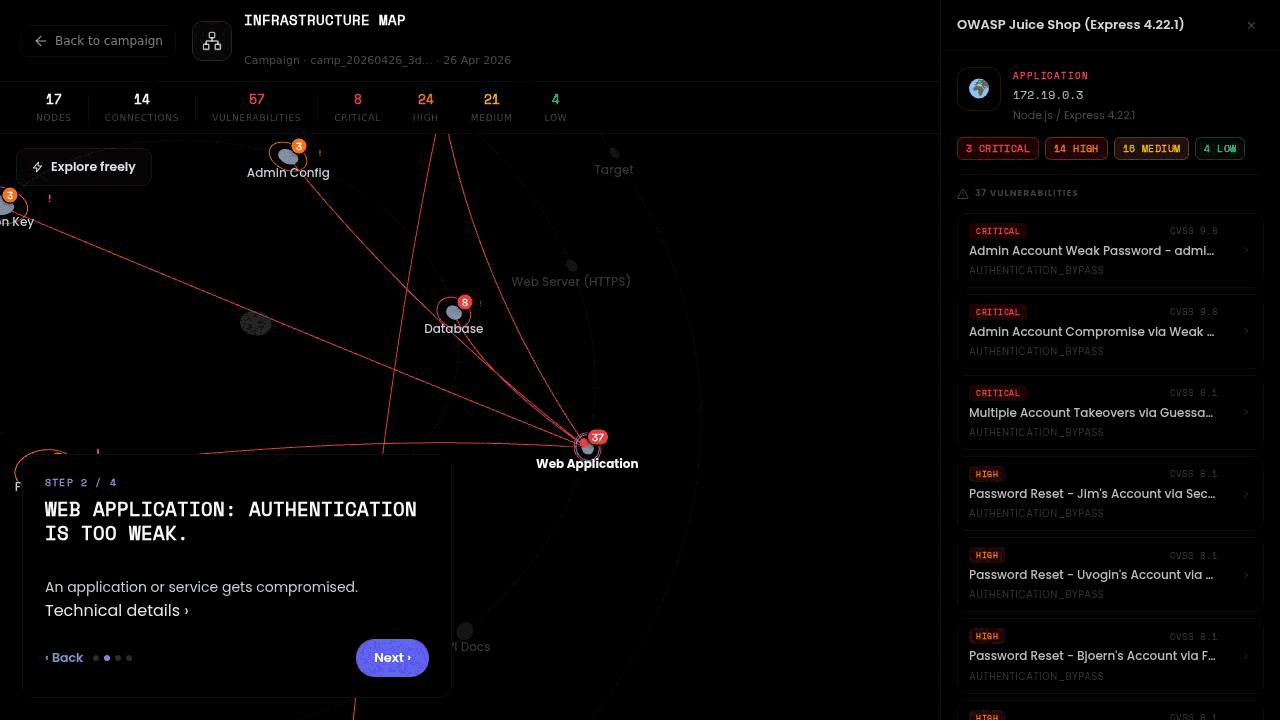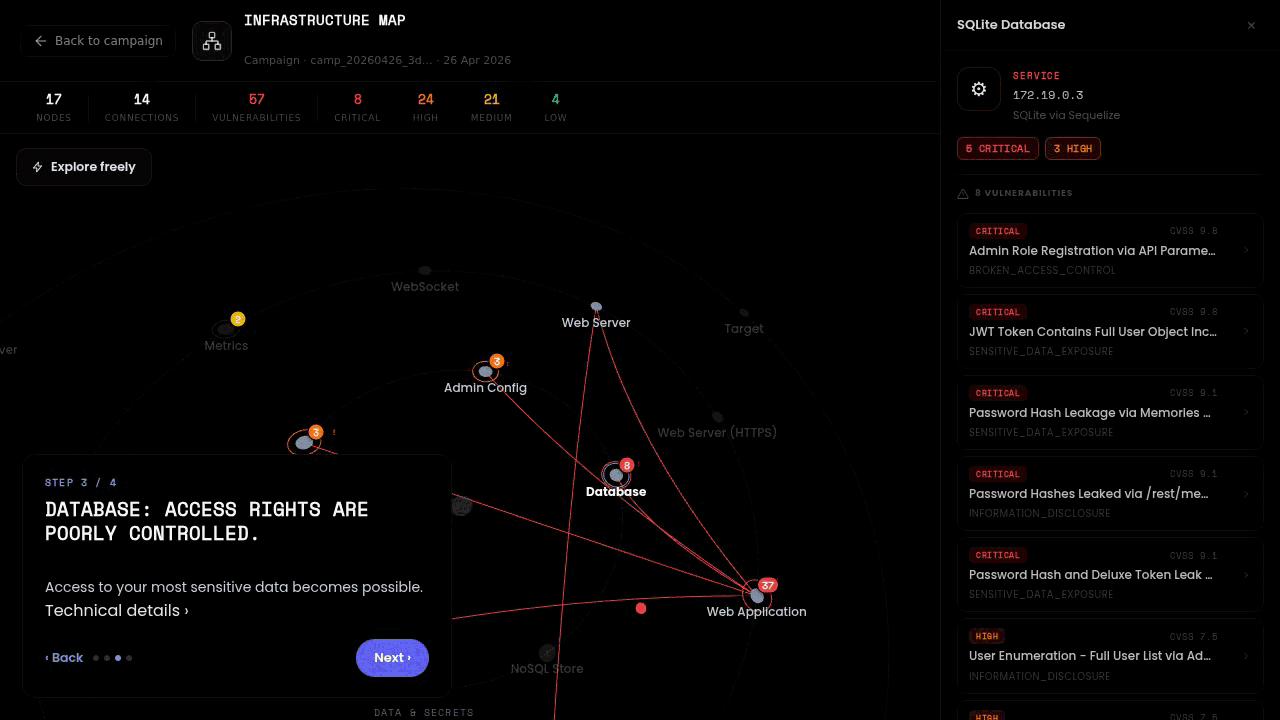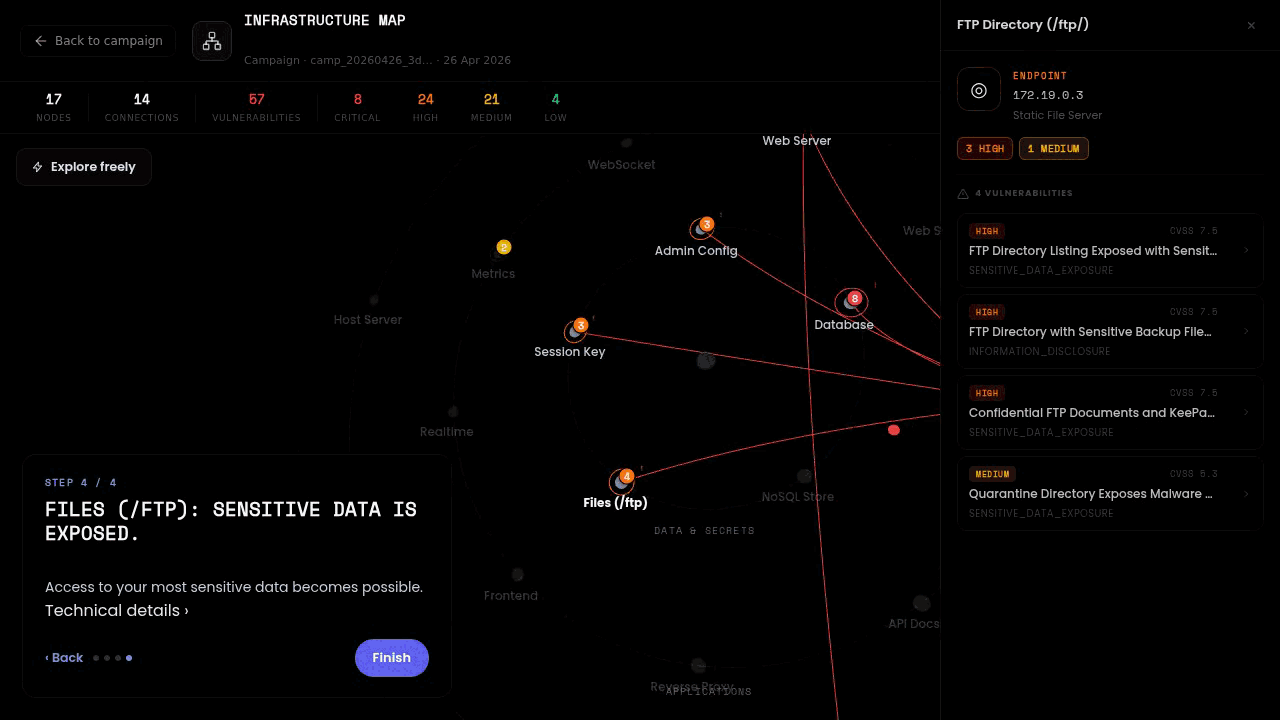
The orbital attack-surface map. Every discovered node, its connections and per-node vulnerabilities, with the MITRE attack path walked across the whole target, and every finding linked to its proposed remediation pull request. In the browser, and over WebXR in a VR headset.
|
|
|
|
| Repository | What it is |
|---|---|
| Dark-Moon | The platform. 50 agents, 50+ offensive tools orchestrated over MCP, Privacy Gateway, CI/CD native. git clone and run your first assessment in minutes. |
| darkmoon-scan-action | GitHub Action that runs the open-source engine in your pipeline. No license needed. Findings land as artifacts. |
| Darkmoon-Benchmarks | Open, reproducible benchmark of autonomous AI pentesters on public vulnerable labs. 57 real vulnerabilities on OWASP Juice Shop in 28.5 minutes, on a local LLM. |
| darkmoon-research | Evidence corpus: runs across cloud, identity, CI/CD, IaC, data and IoT firmware, validated on public labs. |
| Dark-Moon-CI-Demo | A demo pentest pipeline you can fork to see the Action in motion. |
| Awesome-AI-Penetration-Testing | Curated list of AI and LLM powered pentesting tools, platforms, benchmarks and research. |


Numbers refreshed daily from the GitHub API by a scheduled workflow.
|
|
Contributors Every agent's methodology is plain Markdown you can read, diff and fork. Contributions welcome: new agents, tools, benchmarks, translations. Start with the contributing guide and the good first issues.
|


|
Penetration testing of web apps and APIs, Active Directory (Kerberos, privileged accounts, GPO and delegations), networks and IoT. Scoped, executed and reported with CVSS scoring and an encrypted video debrief. |
AWS, Azure and GCP security audits: IAM and identities, storage and data, network, logging, compliance. Kubernetes and container hardening, configuration review, remediation and continuous securing. |
Web and desktop applications, DevSecOps pipelines, AI agent platforms. Angular, NestJS, Next.js, Python, on Kubernetes. Fixed-price builds and long-term maintenance. |

 Aurélien Strich Co-founder · Product Owner, Cybersecurity project lead Ex Marlink, Kratos, Sierra Wireless, CNRS. Speaker at KubeCon EU 2024. 
|
 Mehdi Boutayeb Co-founder · Cybersecurity & AI architect, Lead Engineer, Darkmoon Ex Airbus (AI agent platform), Pierre Fabre. Designed the MCP host, the offensive agents and the Privacy Gateway. 
|
 Vincent Mahaux Sales director, Cybersecurity Scopes engagements, runs the Pentest on Demand offer and the partner programme. 
|
 Florian Cardinal Fullstack developer, Tech lead Web dashboard, Front-API and delivery pipeline of Darkmoon Pro. 
|
 Teva Legares System & network administrator Runs the labs (Active Directory, GOAD), the runners and the production stack. 
|

TF1 Info · Help Net Security · Cyber Security News · DevOps.com · SecurityBrief UK · LinuxFr.org · LinuxSecurity · LinuxLinks · UnderNews · ScanNetSecurity (JP) · OpenNHP · Product Hunt
Listed in Help Net Security's hottest open-source security tools of the month (June 2026).

|
🧑💻 Contribute
Open an issue, send a PR, add an agent or a tool. Read each agent's methodology in |
🔐 Report a vulnerability Found something in Darkmoon or on our infrastructure? Please follow our security policy. No public issues for security reports. |
🤝 Work with us Pentest, cloud audit, DevSecOps or a product to build: asc-it.fr · Darkmoon Pro, Pentest on Demand and the partner programme: dark-moon.org. |


SARL ASC · Toulouse, France · Cybersecurity, conception and software development since 2018 · You just have to ask it.